Email Infrastructure Threat Taxonomy
Taxonomies › Email infrastructure
This is the reference for the Elevation of Email Flow card game: every card’s threat, the mitigation principle a sound design follows, design measures, and mappings to STRIDE, CAPEC and CWE.
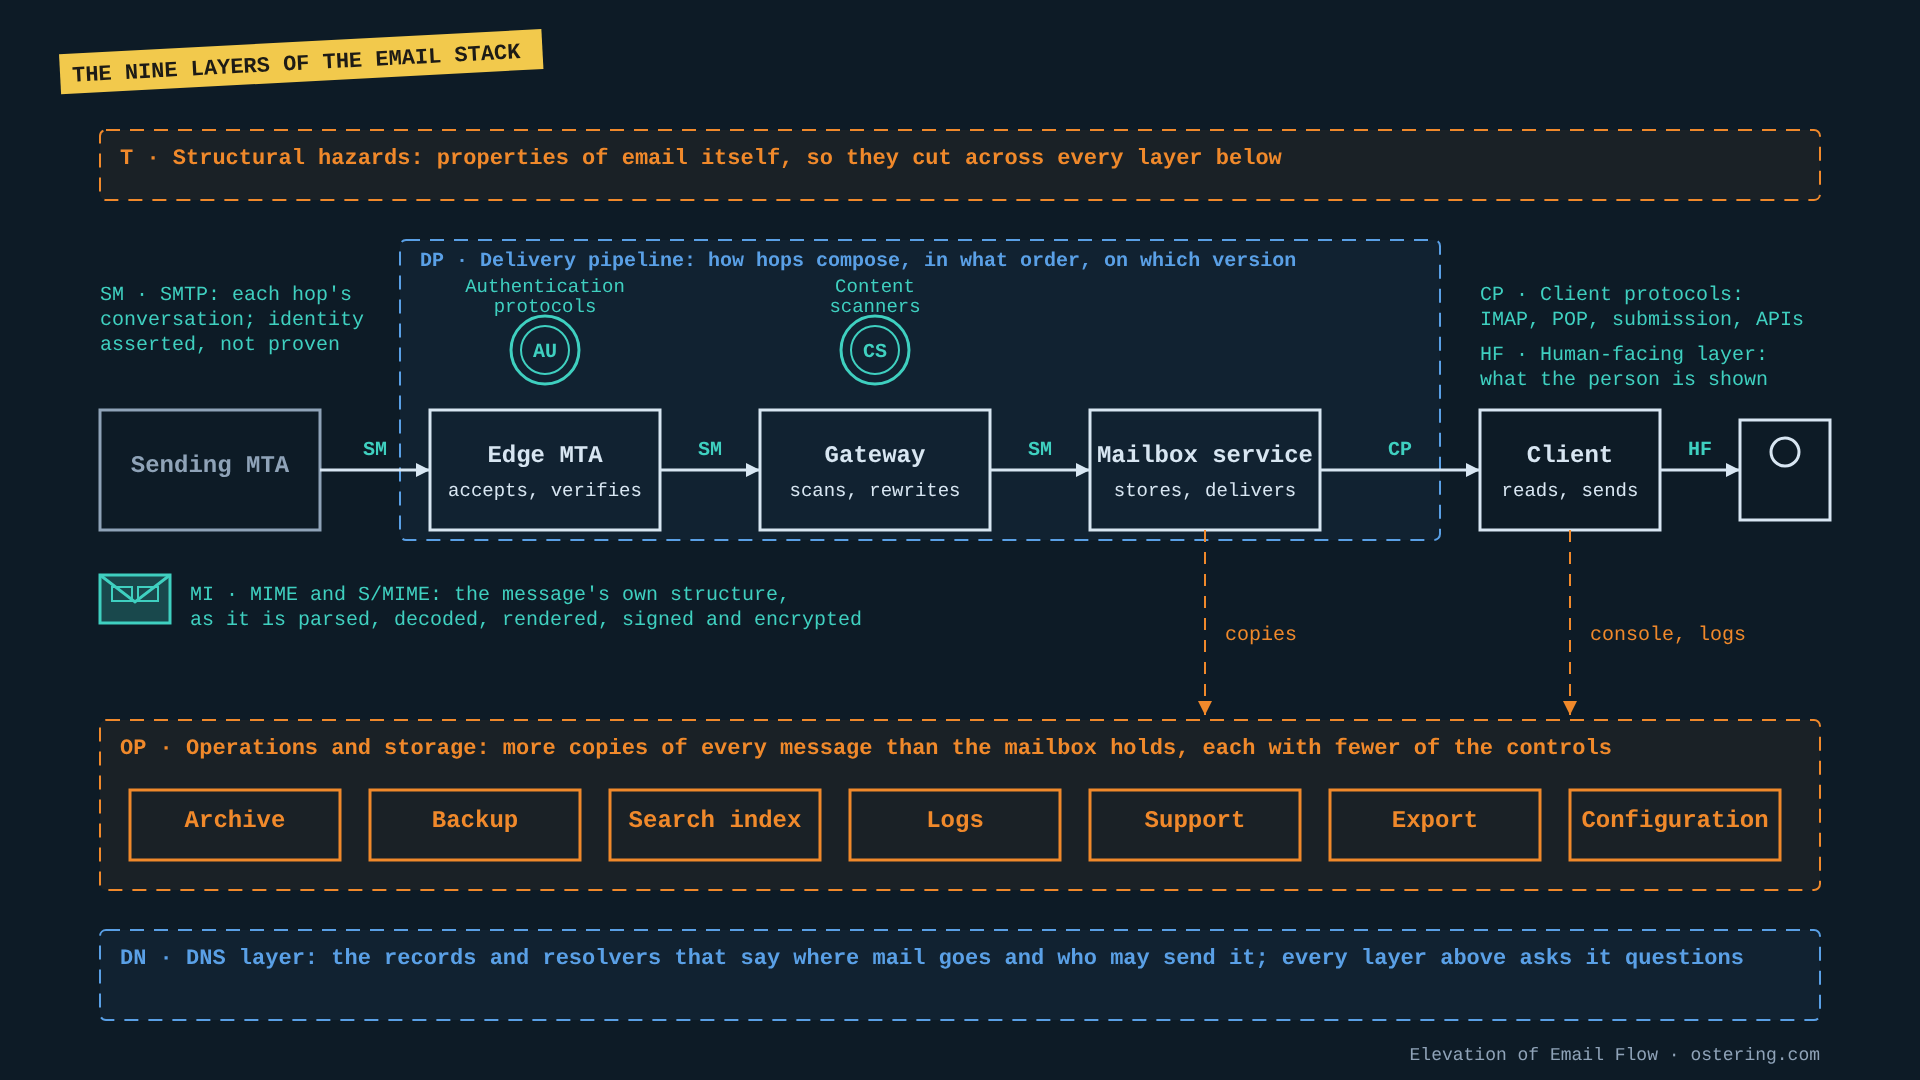
Email infrastructure is the machinery that delivers a message: the SMTP conversation, sender authentication, DNS, MIME parsing, the delivery pipeline, the content scanners, the stores and the clients. This taxonomy catalogues what can go wrong in it: 119 threats across nine layers of the email stack, plus twelve structural hazards, each with the principle a sound design follows and concrete measures that put it into practice.
Every entry is one of the game’s cards, written out so that it can also be used without the game, and the taxonomy card in the game’s box links here with a QR code. Why the taxonomy exists, and what the existing frameworks miss, is in The Unmodeled Attack Surface.
The layers
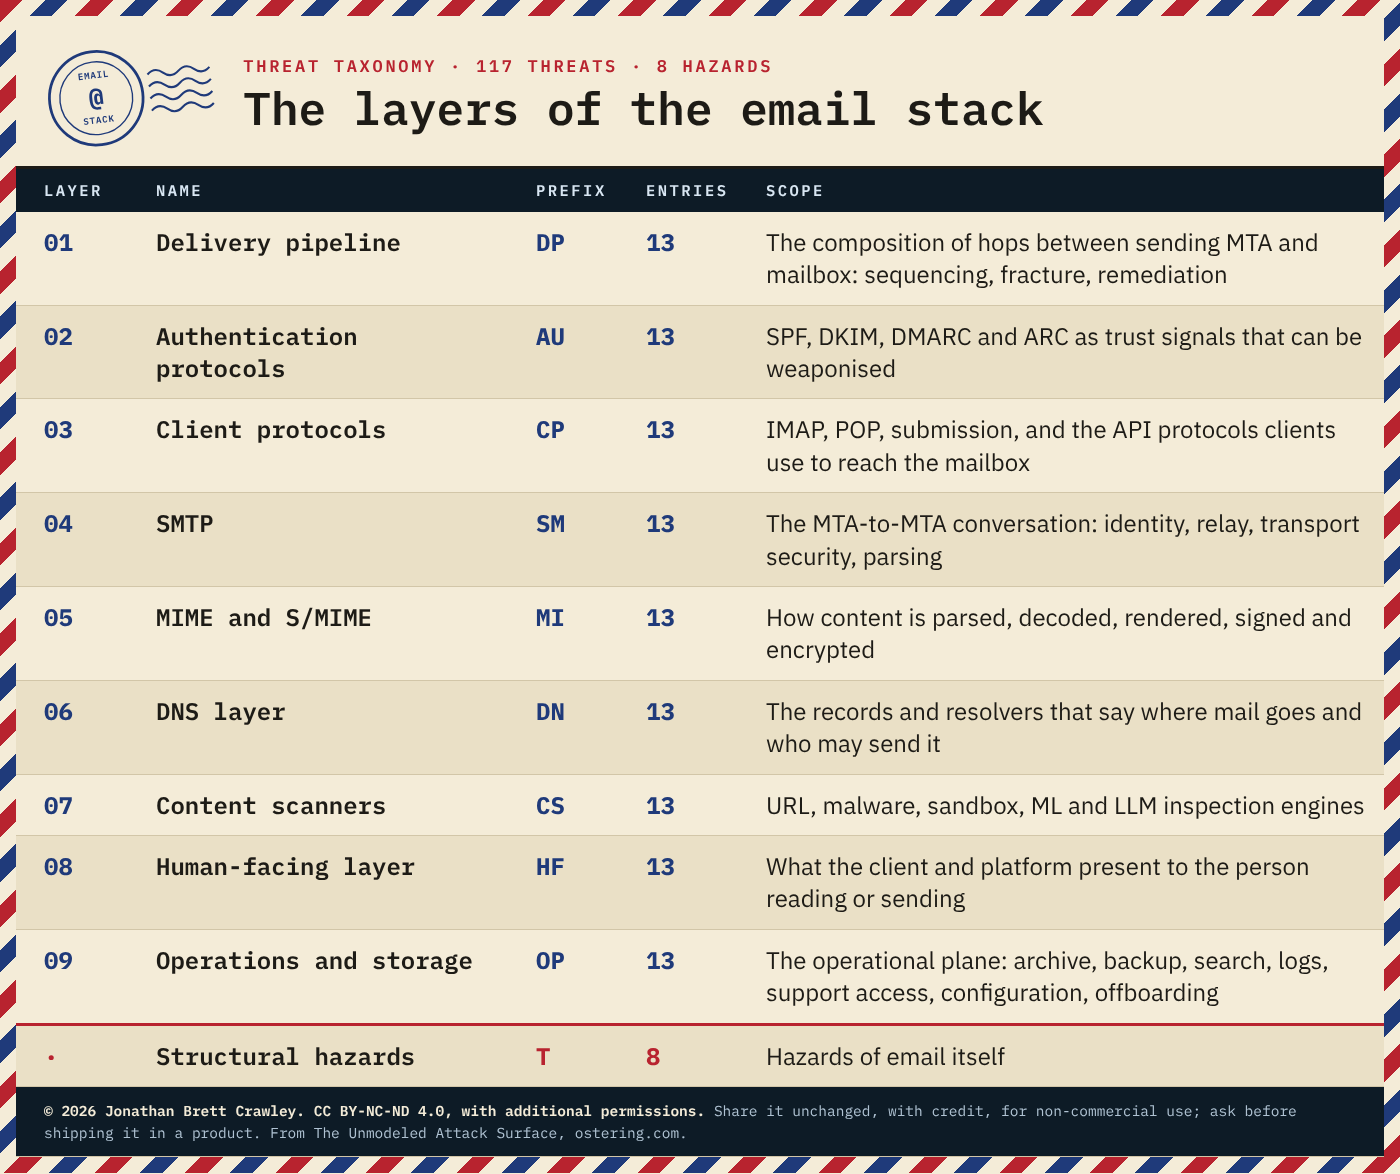
01 · Delivery pipeline (DP): 13 threats. The composition of hops between sending MTA and mailbox: sequencing, fracture, remediation.
02 · Authentication protocols (AU): 13 threats. SPF, DKIM, DMARC and ARC as trust signals that can be weaponised.
03 · Client protocols (CP): 13 threats. IMAP, POP, submission, and the API protocols clients use to reach the mailbox.
04 · SMTP (SM): 13 threats. The MTA-to-MTA conversation: identity, relay, transport security, parsing.
05 · MIME and S/MIME (MI): 13 threats. How content is parsed, decoded, rendered, signed and encrypted.
06 · DNS layer (DN): 13 threats. The records and resolvers that say where mail goes and who may send it.
07 · Content scanners (CS): 13 threats. URL, malware, sandbox, ML and LLM inspection engines.
08 · Human-facing layer (HF): 13 threats. What the client and platform present to the person reading or sending.
09 · Operations and storage (OP): 15 threats. The operational plane: archive, backup, search, logs, support access, configuration, offboarding. The whole stack
Structural hazards (T): 12 hazards. Hazards of email itself.
What an entry contains
- A name, short enough to say in a design review.
- A threat, stated as a property of a component or a design decision. Not “an attacker could”, but “the platform does”.
- A mitigation principle: what a sound design does, stated so that different designs can satisfy it in different ways.
- Design measures: two to four concrete ways of satisfying the principle. They are examples of what works, not the only acceptable answers. The format is deliberate. A threat on its own is an accusation, and a list of measures on its own is a checklist that fits one architecture and no other. The principle sits between them: it says what must be true, and the measures show what that looks like in practice. Against a real design, each entry produces a finding, or a one-line “no exposure” with the reason, which is worth writing down too.
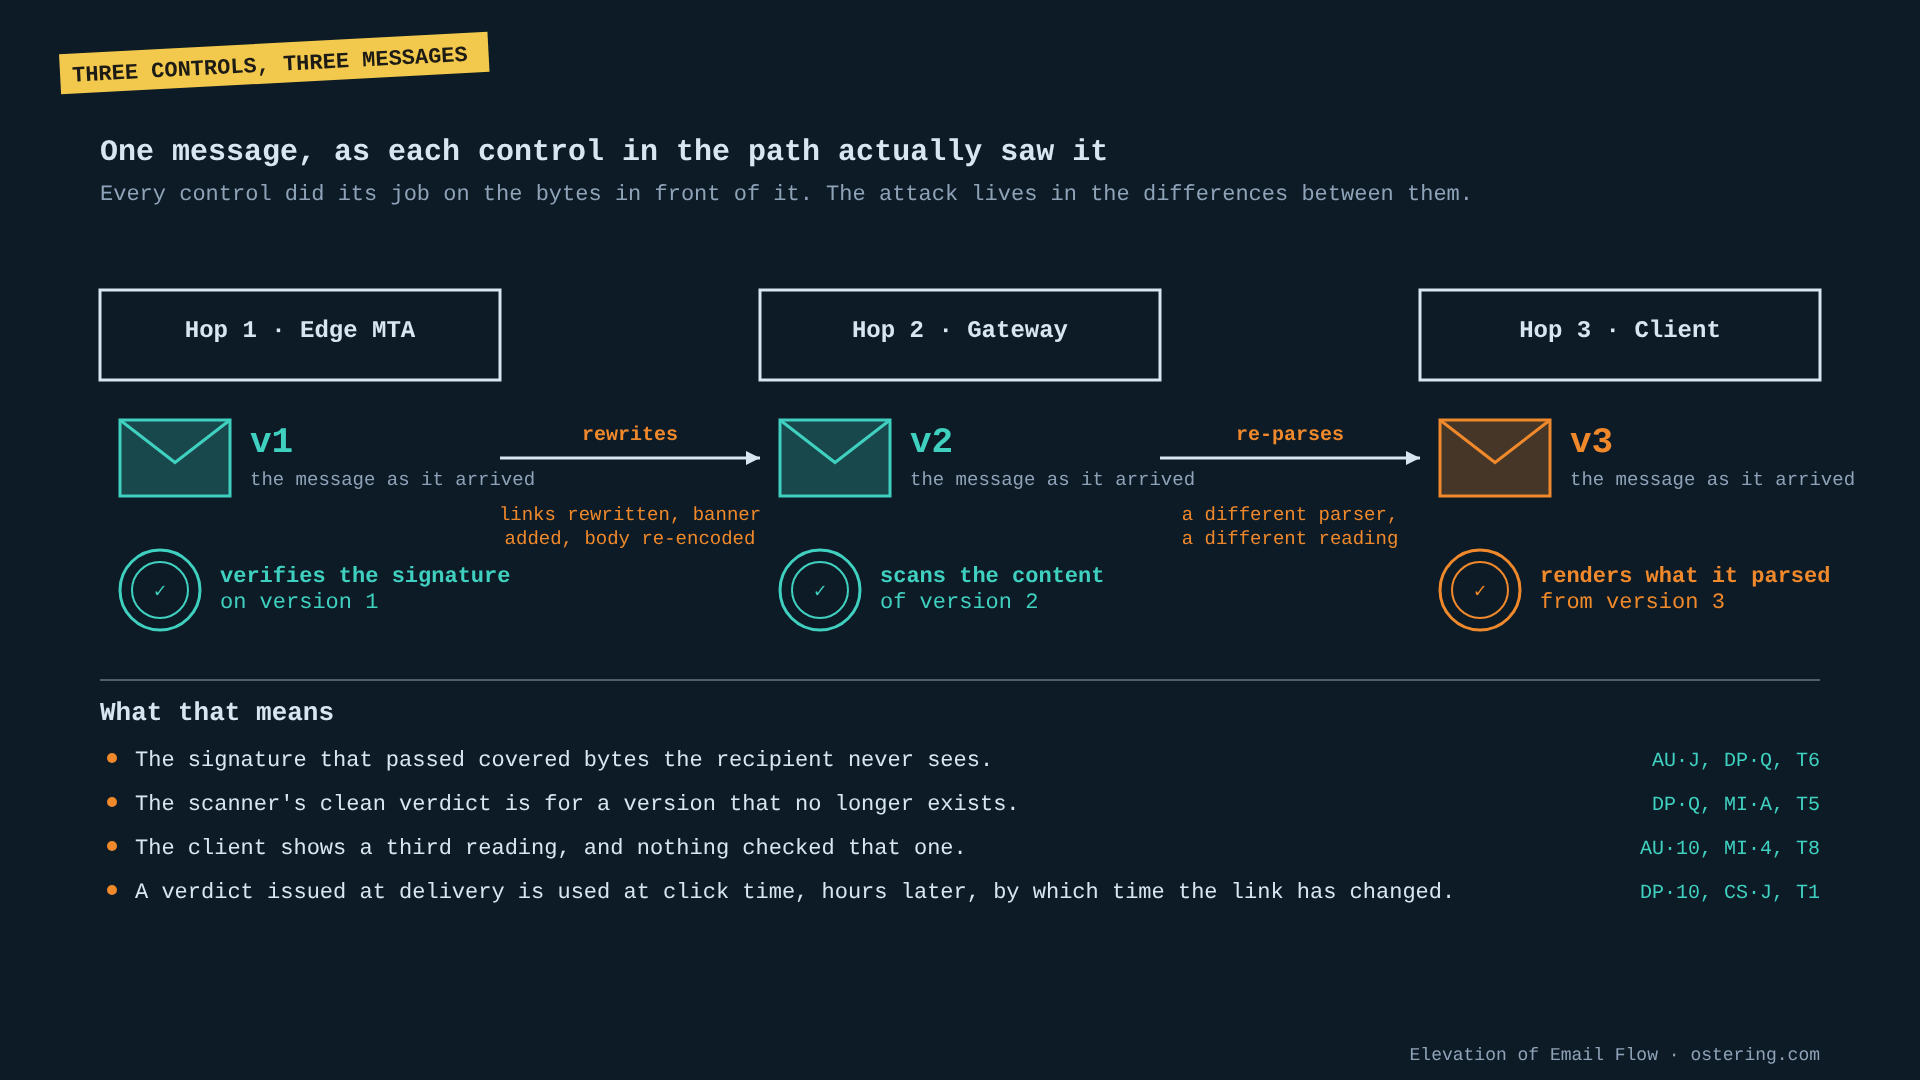
What the taxonomy assumes. It maps email as it is deployed: a message passes through a sequence of components, and every control in that sequence works by reading the message. That reader at every hop is the terrain, not a choice any one platform made, and most of the entries harden the readers rather than question them. EM-T9, The Reader in the Middle, is where the assumption itself is treated as the hazard: it asks where plaintext exists, who can read it, and whether each control could work on less. EM-T3, EM-T4 and EM-T7 are consequences of it, and EM-MI-9, EM-OP-A and EM-OP-7 point back to it. A reviewer of the first version made the point that the taxonomy named the symptoms and not the fact beneath them; EM-T9 is the response.
Each entry carries a reference such as EM-DP-J or EM-T2: EM for this taxonomy, then the layer prefix and a playing-card rank, from Ace down to 2, or T1 to T11 for the structural hazards. A point, as in EM-OP-10.1 or EM-T2.1, marks a sub-entry of the entry above it, added after the first edition; in the game it is a card that ranks just below its parent. The EM prefix keeps references from different taxonomies apart, and the dashes keep a reference in one piece when a search engine, a spreadsheet or a tool indexes it. The taxonomy is the reference for the card game Elevation of Email Flow: each entry is one of its cards, and the card carries the same reference. The reference is a stable identifier, not a severity. In the game the ranks follow severity, because play is trick-based; here a reference only names an entry, and it stays the same as the taxonomy grows.
How to use it
- Draw the mail flow: every hop, scanner, store and client a message touches, with the trust boundaries marked.
- Take one layer and walk every entry in it against each element it applies to.
- For each entry, ask whether the design satisfies the principle. Write down a finding, or “no exposure” and the design decision that defeats it.
- Where there is a finding, start from the measures given and adapt them to your architecture. They are the shape of a fix, not a prescription.
- Finish with the structural hazards, played against the design as a whole. They usually explain several findings at once and point to an architectural change, not a patch per finding. Note to platform builders: start with the delivery pipeline. Every other layer assumes the message actually passed the controls, and that is the assumption to test first.
Each layer page shows its entries as a table graphic. The downloads carry the same content as text that can be searched, filtered and copied.
Where layers touch
Some layers touch, and it helps to know which side of the line an entry sits on:
- Authentication and DNS: DNS covers who can control or falsify an answer. Authentication covers what a genuine answer can be made to mean.
- SMTP and delivery pipeline: SMTP is a single hop’s conversation. The pipeline is the composition of hops.
- MIME and delivery pipeline: MIME is how a message is interpreted. The pipeline is whether and when it is inspected.
- Delivery pipeline and content scanners: the pipeline decides what to do with a scanner’s limits and verdicts. The scanner layer asks whether the inspection itself holds up.
- Tenancy: Tenant Confusion (EM-DP-7), Cross-Tenant Identity (EM-AU-K) and Shared Reputation Poisoning (EM-SM-8) each cover a different face of shared infrastructure (configuration, identity, reputation). Shared Infrastructure, Shared Fate (EM-T2) is the structural hazard behind all three.
- Availability: What happens when the platform says no is split by who owns the decision. Delay Becomes Loss (EM-T11) and Suppression After Outage (EM-T10) are hazards: they sit on the sender’s queue and the sender’s suppression list, which the receiver does not own. False Rejection (EM-OP-10.1) and Control-Plane Blackout (EM-OP-5.1) are the platform’s own operational decisions, a change that goes live unreviewed and a console that shares fate with the data plane, so they sit under their parents in operations and storage. Shared Infrastructure, Shared Outage (EM-T2.1) is the pipeline’s concentration (EM-DP-2, EM-DP-6). Resource Exhaustion (EM-SM-6) is the effect each of them produces.
- Readers: MIME and S/MIME (EM-MI-9), the content scanner layer and operations and storage (EM-OP-A, EM-OP-7, EM-OP-Q, EM-OP-6) each assume a component that holds plaintext. The Reader in the Middle (EM-T9) is the structural hazard behind all of them: the control and the exposure are the same component.
- Operations and the other layers: delivery pipeline, client protocols and DNS each cover a corner of operations (admin routing changes in EM-DP-2, mailbox state in EM-CP-10, dangling records in EM-DN-K). Operations and storage covers the stores and tooling around the message path: the copies, the credentials and the people with access.
Scope and origin
The taxonomy does not cover social engineering, phishing lures or the human decisions that make email such a successful attack vector. Those threats are real, well documented and served by existing frameworks. It covers the infrastructure: the components, protocols and sequencing contracts that deliver the message. That layer had no dedicated taxonomy.
It started as a game. I designed Elevation of Email Flow, a threat modeling card game, because I saw a gap in the games we already have: they cover web applications, cloud, privacy and more, but none of them covers email infrastructure. The deck came first, and this taxonomy is its reference: each card’s threat became an entry, each card’s suit became a layer, and the mitigation principle and measures were written to answer the questions the card asks. This taxonomy is the game’s content, restated so that it can be used without the game.
I want to be clear about one thing: it is not that these issues did not exist. They were already known, publicly disclosed in real systems. SMTP smuggling, EFAIL, the composition attacks on sender authentication and the large-scale spoofing studies are well-known examples; the sources below point to the original disclosures. What was missing was the translation. Each issue had to be restated as a threat that a designer can test their own system against, and the whole lot collated into a single resource. That is the contribution here: the translation and the collection, not the discovery.
STRIDE, CAPEC and CWE
Every entry is mapped to STRIDE and to CAPEC 3.9. STRIDE fits 75 of the 131 entries cleanly and 56 only loosely. CAPEC has a pattern that describes 31 directly, only a generic parent for 66, and nothing for 34. What the mapping shows is in Mapping the Email Threat Taxonomy to STRIDE, CAPEC and CWE. Every entry is also mapped to CWE 4.20, the catalogue of software weaknesses: a CWE weakness names the flaw directly for 68 entries, only a broader weakness applies to 56, and CWE has nothing for 7. Each layer page gives its own figures and its mapping table, entry by entry; the Excel, SKOS and STIX downloads carry every mapping as text.
Downloads
| Download | Format | What it is for |
|---|---|---|
| A4 landscape, a section per layer, with each entry’s STRIDE, CAPEC and CWE mapping | Reading and printing. Also the text version of the tables on these pages. | |
| Excel | Workbook, one layer per sheet | Filtering, sorting, copying entries into a threat model, tracking findings. |
| SKOS (JSON-LD) | W3C SKOS concept scheme | Linked data: the hierarchy, references, mitigations, and links to STRIDE, CAPEC and CWE. |
| STIX 2.1 | STIX 2.1 bundle | Security tooling: an attack pattern and a course of action per entry, grouped by layer, with CAPEC and CWE references. |
All four carry the licence. The STIX bundle’s extra fields are described by this JSON Schema.
Licence
© 2026 Jonathan Brett Crawley. This taxonomy is licensed under the Creative Commons Attribution-NonCommercial-NoDerivatives 4.0 International licence (CC BY-NC-ND 4.0), with the additional permissions below. You can share the whole taxonomy freely for non-commercial purposes, unchanged and with credit.
| Use | Permission needed? |
|---|---|
| Sharing the whole taxonomy non-commercially (OWASP, universities, conferences, individuals) | No |
| Threat modeling with it, including for paying clients | No |
| Internal use and training inside any organisation | No |
| Quoting entries, with credit, in paid courses, reports and talks | No |
| Shipping the taxonomy in a product: a tool’s built-in library, a printed deck, a reprint for sale | Yes, ask me |
Additional permissions. In addition to the rights the licence gives, and whether or not the use is commercial, the copyright holder grants you permission to:
- Use the taxonomy to threat model systems you build, operate or assess, including for paying clients;
- Use it internally, and for training, inside any organisation;
- Quote individual entries, with credit, in paid courses, reports, findings and talks. Any other commercial use, including shipping the taxonomy or a substantial part of it in a product (a tool’s built-in library, a printed deck, a reprint for sale), needs written permission. Ask me on LinkedIn.
Credit: “Email Infrastructure Threat Taxonomy” by Jonathan Brett Crawley, ostering.com, licensed under CC BY-NC-ND 4.0.
These additional permissions are given alongside the licence. They add to what the licence allows and do not take anything away from it.
Version
| Version | Date | Change |
|---|---|---|
| 1.0 | 26 October 2026 | First published as reference pages, with PDF, Excel, SKOS and STIX downloads. References are stable identifiers. |
| 1.1 | 2 November 2026 | References namespaced by taxonomy and joined with dashes (EM-DP-A, EM-T8) so that they index as one token; each entry keeps its old anchor. |
| 1.2 | 3 November 2026 | The Elevation of Email Flow cards print the same reference, so the separate card code was dropped from the downloads. |
| 1.3 | 6 November 2026 | EM-T9, The Reader in the Middle, added as the ninth structural hazard after review feedback. EM-MI-9 reworded with a measure added; measures added to EM-OP-A, EM-OP-7, EM-T3, EM-T4 and EM-T7 that point to it; a Readers note under where layers touch. Table images, mapping figures and all four downloads rebuilt. |
| 1.4 | 14 November 2026 | Five structural hazards added after the Exchange Online outage of 12 to 14 November 2026: EM-T13 Delay Becomes Loss, EM-T12 Suppression After Outage, EM-T11 Control-Plane Blackout, EM-T10 False Rejection and EM-T2.1 Shared Infrastructure, Shared Outage. An Availability note under where layers touch. 131 entries. Table images, mapping figures and all four downloads rebuilt. |
| 1.5 | 14 November 2026 | Same day as 1.4, after review: False Rejection and Control-Plane Blackout move from the Trumps to operations and storage as sub-entries EM-OP-10.1 and EM-OP-5.1, below Unreviewed Configuration Change and Audit Gap; the remaining availability hazards are renumbered EM-T11 Delay Becomes Loss and EM-T10 Suppression After Outage. Sub-entry convention stated. Delay Becomes Loss cross-references EM-T9. 119 threats in nine layers, twelve hazards, 131 entries. Table images, mapping figures and all four downloads rebuilt. |
Corrections, missing threats and worked examples are welcome: reach out to me on LinkedIn. Changes are logged here.
Sources
The issues behind these entries were already publicly disclosed in real systems; the contribution of the taxonomy is the translation into threats a designer can test against, and the collection. These are the original disclosures.
- Timo Longin, SEC Consult Vulnerability Lab, SMTP Smuggling: Spoofing E-Mails Worldwide, 18 December 2023.
- Damian Poddebniak, Christian Dresen, Jens Müller, Fabian Ising, Sebastian Schinzel, Simon Friedberger, Juraj Somorovsky and Jörg Schwenk, Efail: Breaking S/MIME and OpenPGP Email Encryption using Exfiltration Channels, 27th USENIX Security Symposium, 2018.
- Jianjun Chen, Vern Paxson and Jian Jiang, Composition Kills: A Case Study of Email Sender Authentication, 29th USENIX Security Symposium, 2020.
- Kaiwen Shen, Chuhan Wang, Minglei Guo, Xiaofeng Zheng, Chaoyi Lu, Baojun Liu, Yuxuan Zhao, Shuang Hao, Haixin Duan, Qingfeng Pan and Min Yang, Weak Links in Authentication Chains: A Large-scale Analysis of Email Sender Spoofing Attacks, 30th USENIX Security Symposium, 2021.