Orchestration (OR)
Taxonomies › Software factory › Orchestration
Station 16 of 17 · Line 2, Artifact to Runtime · 13 threats · prefix OR
The orchestrator’s API is a remote shell on every node for whoever holds the right role. These cards cover the Kubernetes API, RBAC, admission, operators and Helm, nodes and cluster networking.
Scope: Kubernetes API, RBAC, admission, operators, Helm, nodes, cluster networking.
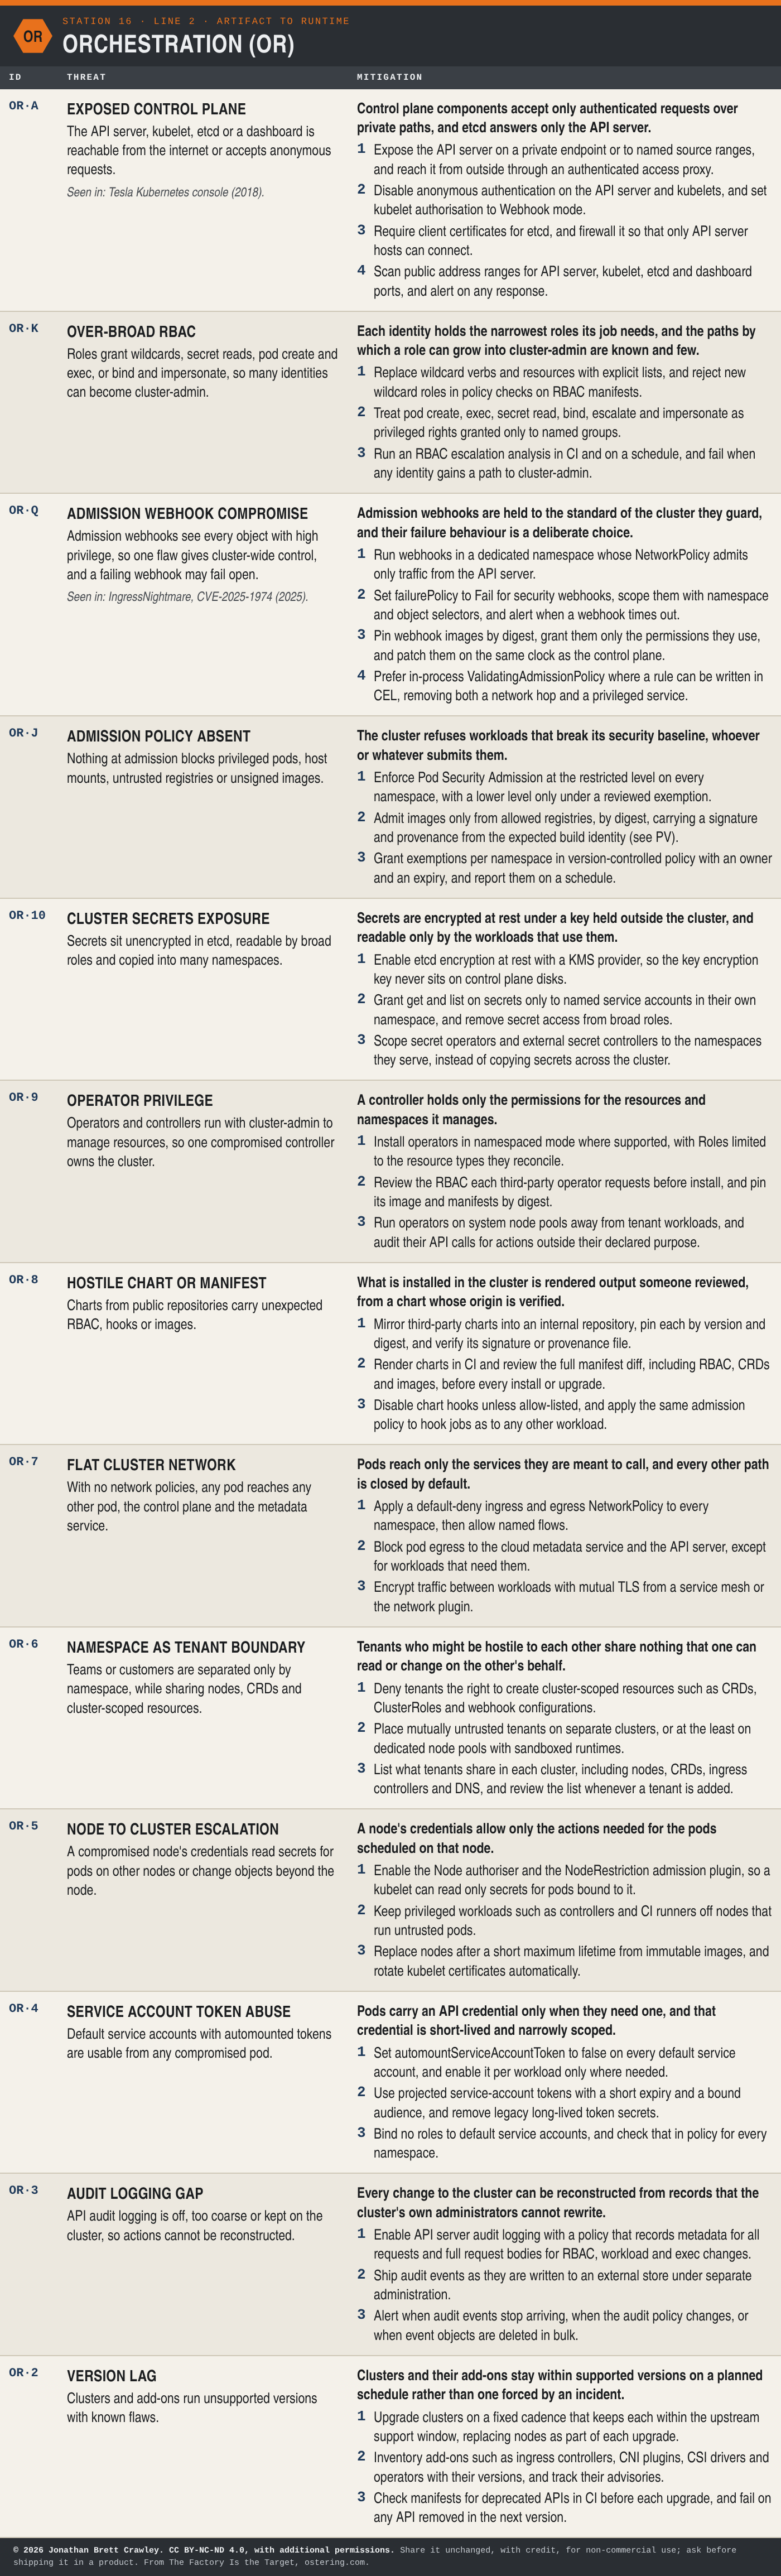
Text version: every entry on this page is in the PDF and Excel downloads on the overview page, where it can be searched and copied.
The threats
- OR·A Exposed Control Plane
- OR·K Over-Broad RBAC
- OR·Q Admission Webhook Compromise
- OR·J Admission Policy Absent
- OR·10 Cluster Secrets Exposure
- OR·9 Operator Privilege
- OR·8 Hostile Chart or Manifest
- OR·7 Flat Cluster Network
- OR·6 Namespace as Tenant Boundary
- OR·5 Node to Cluster Escalation
- OR·4 Service Account Token Abuse
- OR·3 Audit Logging Gap
- OR·2 Version Lag
Where this station touches others
- Orchestration and Delivery and Deployment: orchestration is the cluster that runs workloads; delivery is the path that puts them there.
Seen in the wild
- OR·A Exposed Control Plane: Tesla Kubernetes console (2018).
- OR·Q Admission Webhook Compromise: IngressNightmare, CVE-2025-1974 (2025).
Sources for each case are listed on the overview page.
STRIDE, CAPEC and CWE
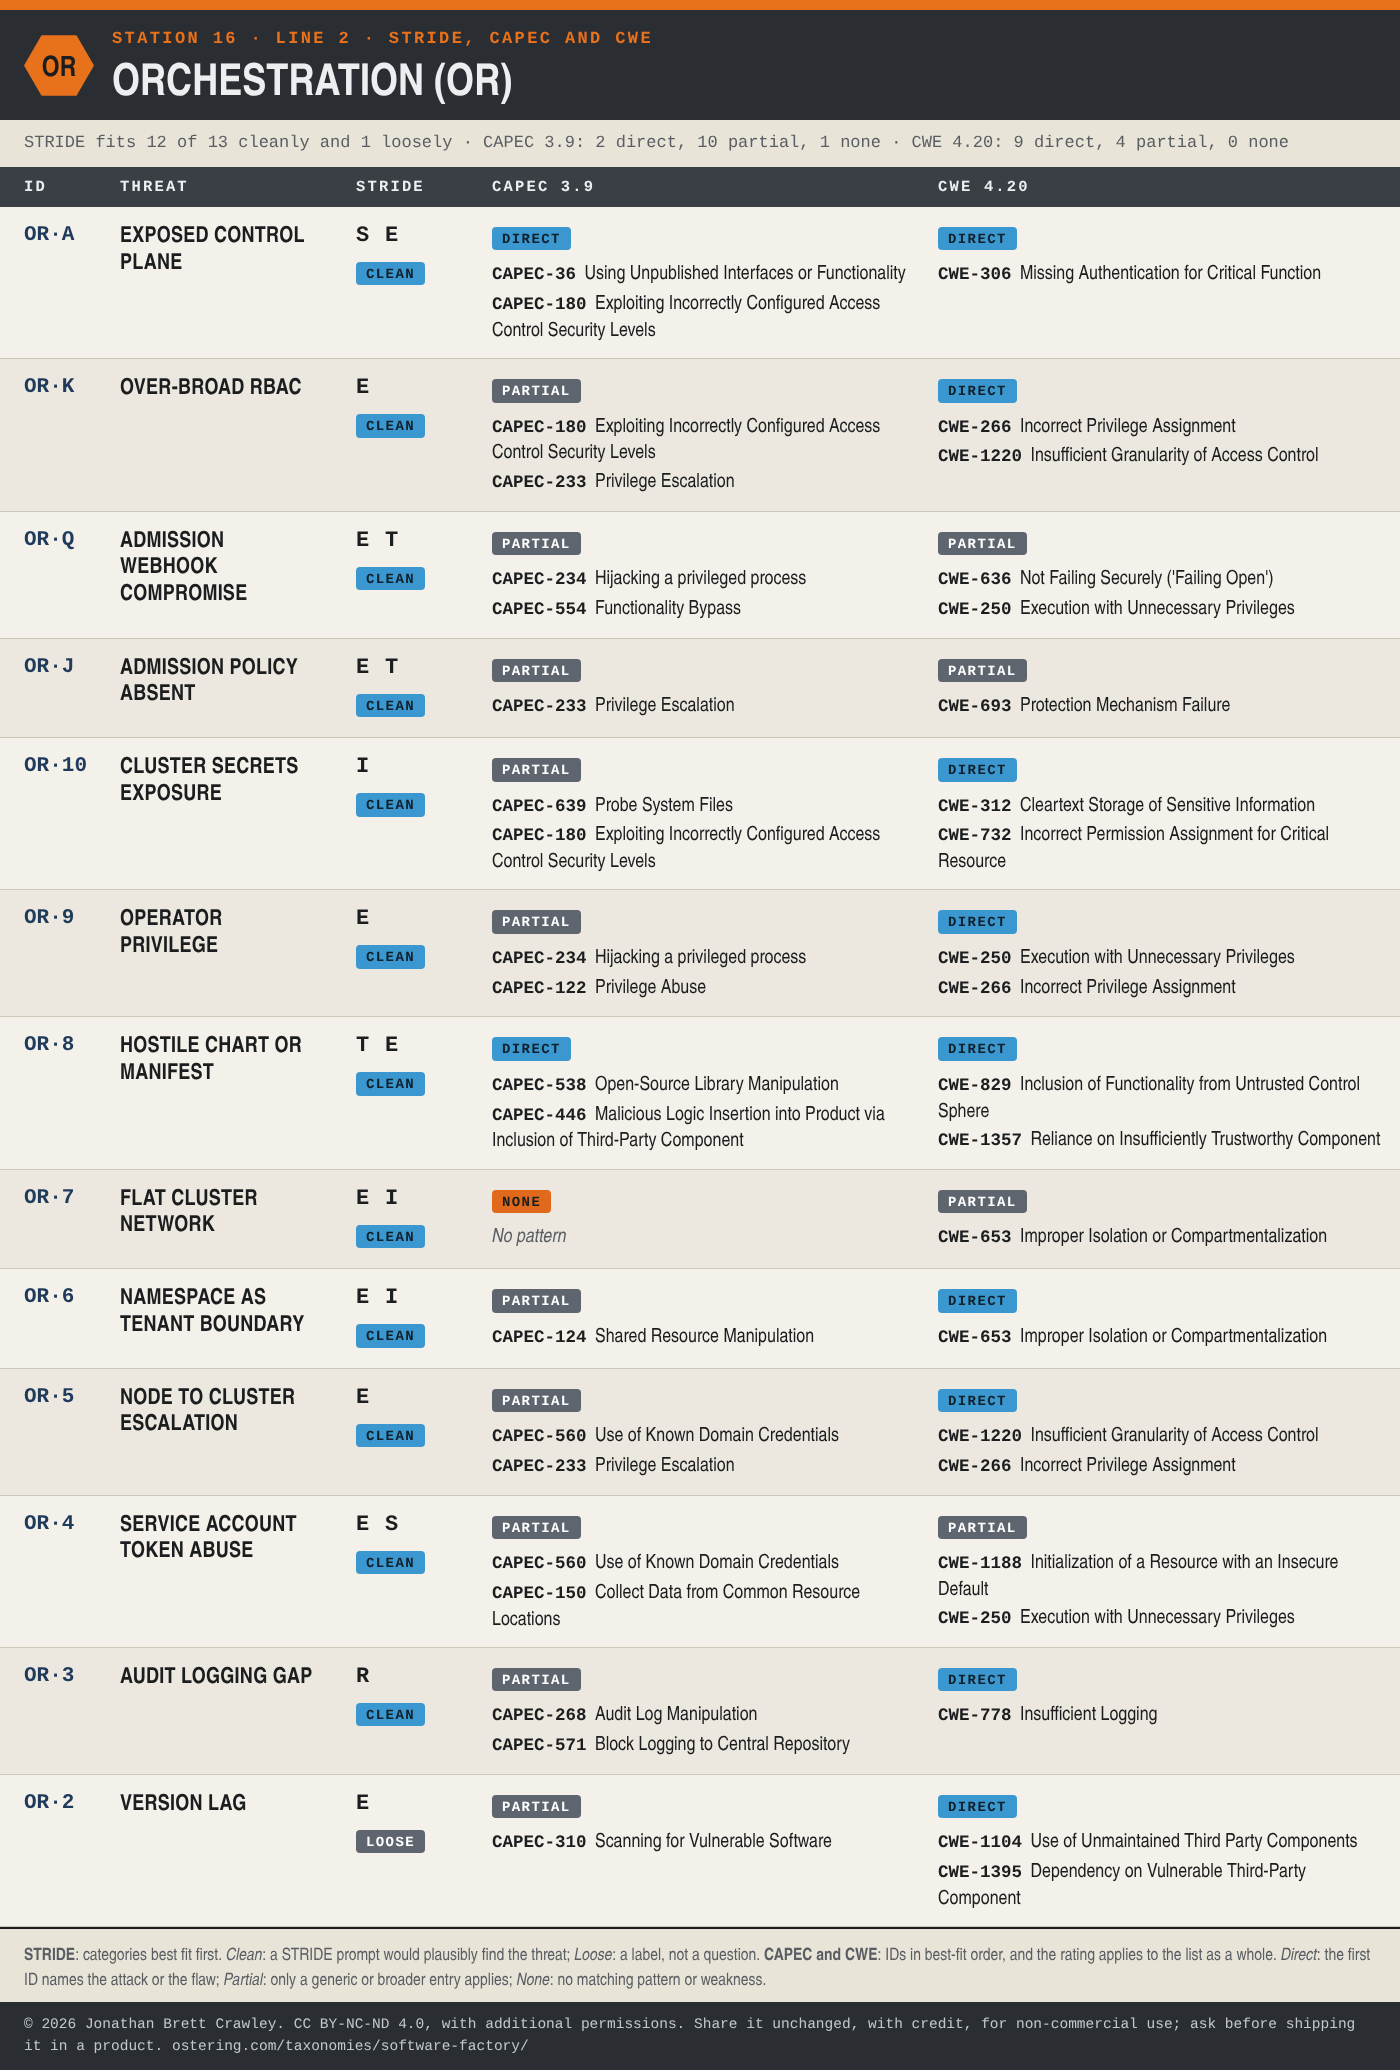
Of the 13 entries here, STRIDE fits 12 cleanly and 1 only loosely. CAPEC 3.9 has a pattern that describes 2 of them directly, only a generic parent pattern for 10, and nothing for 1. CWE 4.20 names the weakness directly for 9, has only a broader weakness for 4,. The table below gives the mapping entry by entry, with the names of the CAPEC patterns and CWE weaknesses; what the mapping shows across the whole taxonomy is in Mapping the Software Factory Threat Taxonomy to STRIDE, CAPEC and CWE. The Excel, SKOS and STIX downloads carry the same mapping as text.
← Container Runtime (RT) · Software factory overview · Delivery and Deployment (DL) →
© 2026 Jonathan Brett Crawley. Licensed under CC BY-NC-ND 4.0 with additional permissions: see the licence on the software factory overview.