Delivery and Deployment (DL)
Taxonomies › Software factory › Delivery and Deployment
Station 17 of 17 · Line 2, Artifact to Runtime · 13 threats · prefix DL
The last hop decides what actually runs, and every earlier control is worth only what this hop enforces. These cards cover CD tools, GitOps controllers, promotion, environments, approvals, rollback and release channels.
Scope: CD tools, GitOps controllers, promotion, environments, approvals, rollback.
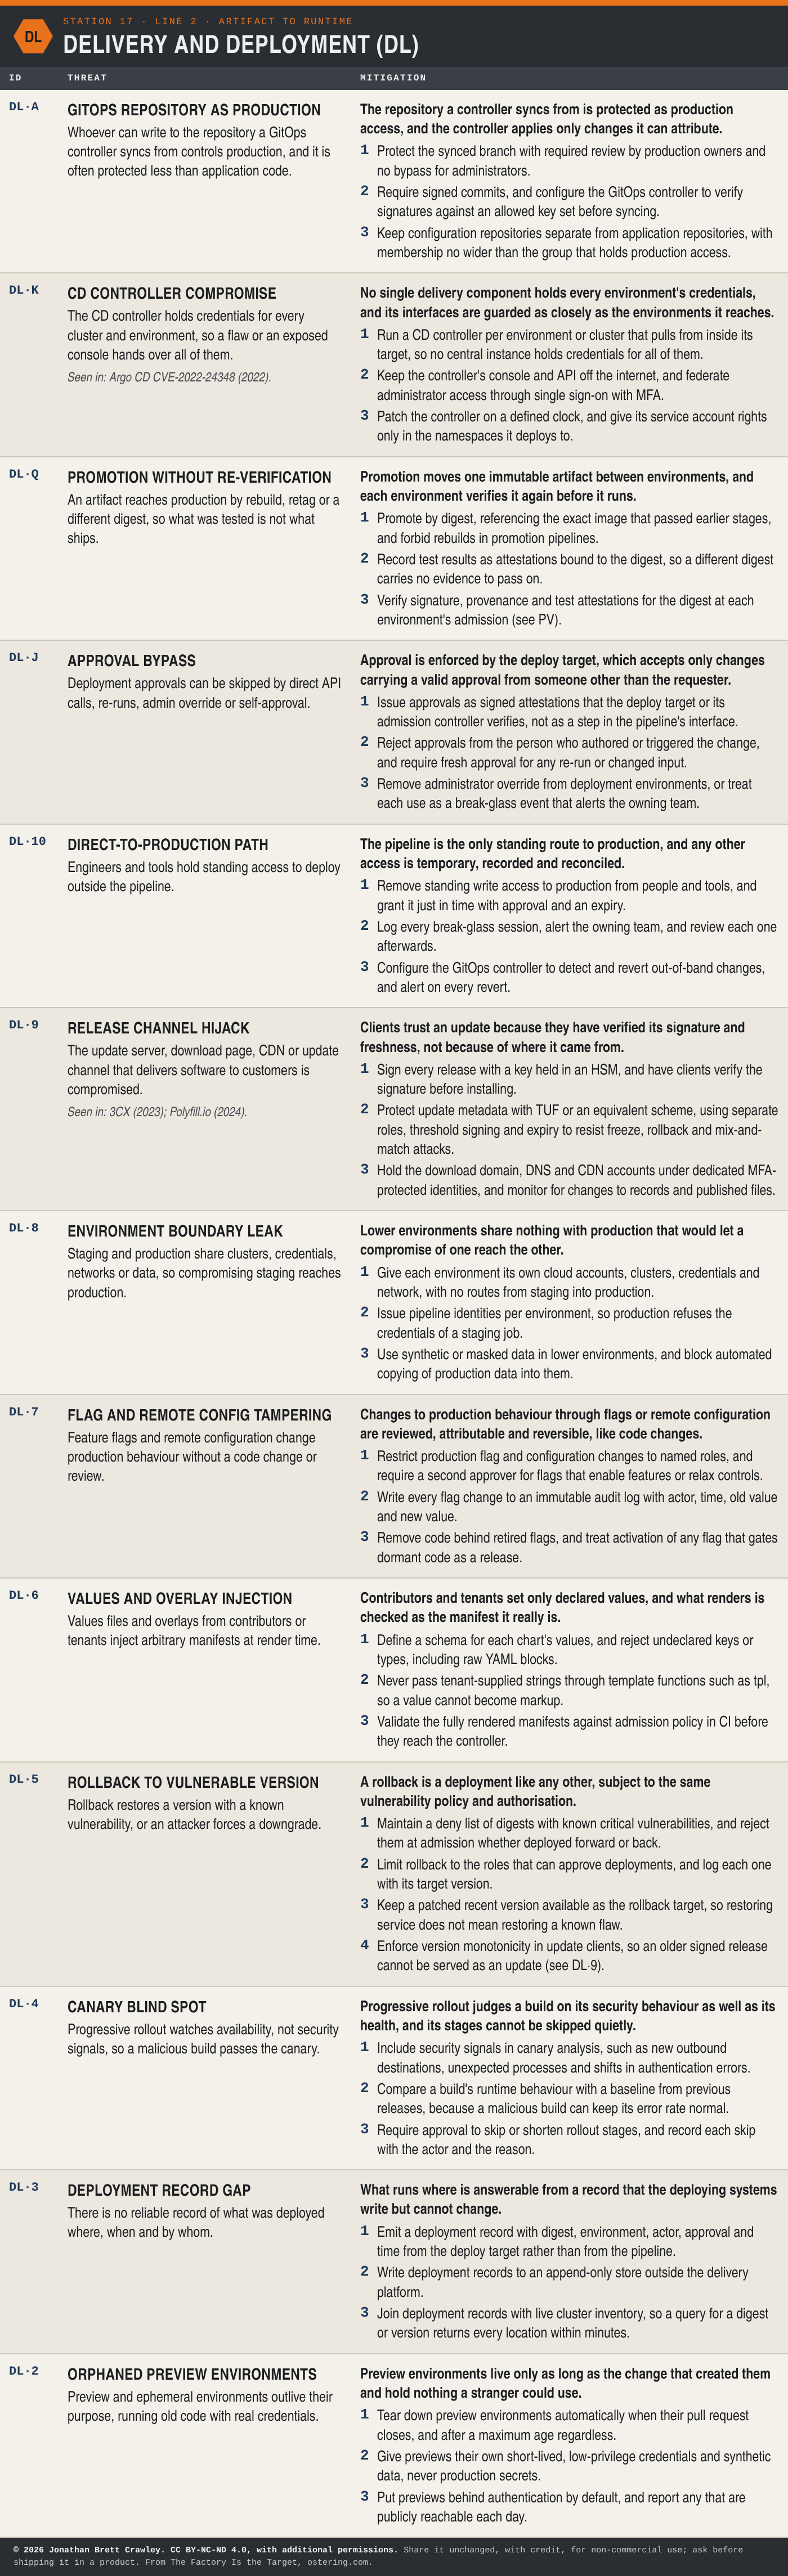
Text version: every entry on this page is in the PDF and Excel downloads on the overview page, where it can be searched and copied.
The threats
- DL·A GitOps Repository as Production
- DL·K CD Controller Compromise
- DL·Q Promotion Without Re-verification
- DL·J Approval Bypass
- DL·10 Direct-to-Production Path
- DL·9 Release Channel Hijack
- DL·8 Environment Boundary Leak
- DL·7 Flag and Remote Config Tampering
- DL·6 Values and Overlay Injection
- DL·5 Rollback to Vulnerable Version
- DL·4 Canary Blind Spot
- DL·3 Deployment Record Gap
- DL·2 Orphaned Preview Environments
Where this station touches others
- Orchestration and Delivery and Deployment: orchestration is the cluster that runs workloads; delivery is the path that puts them there.
Seen in the wild
- DL·K CD Controller Compromise: Argo CD CVE-2022-24348 (2022).
- DL·9 Release Channel Hijack: 3CX (2023); Polyfill.io (2024).
Sources for each case are listed on the overview page.
STRIDE, CAPEC and CWE
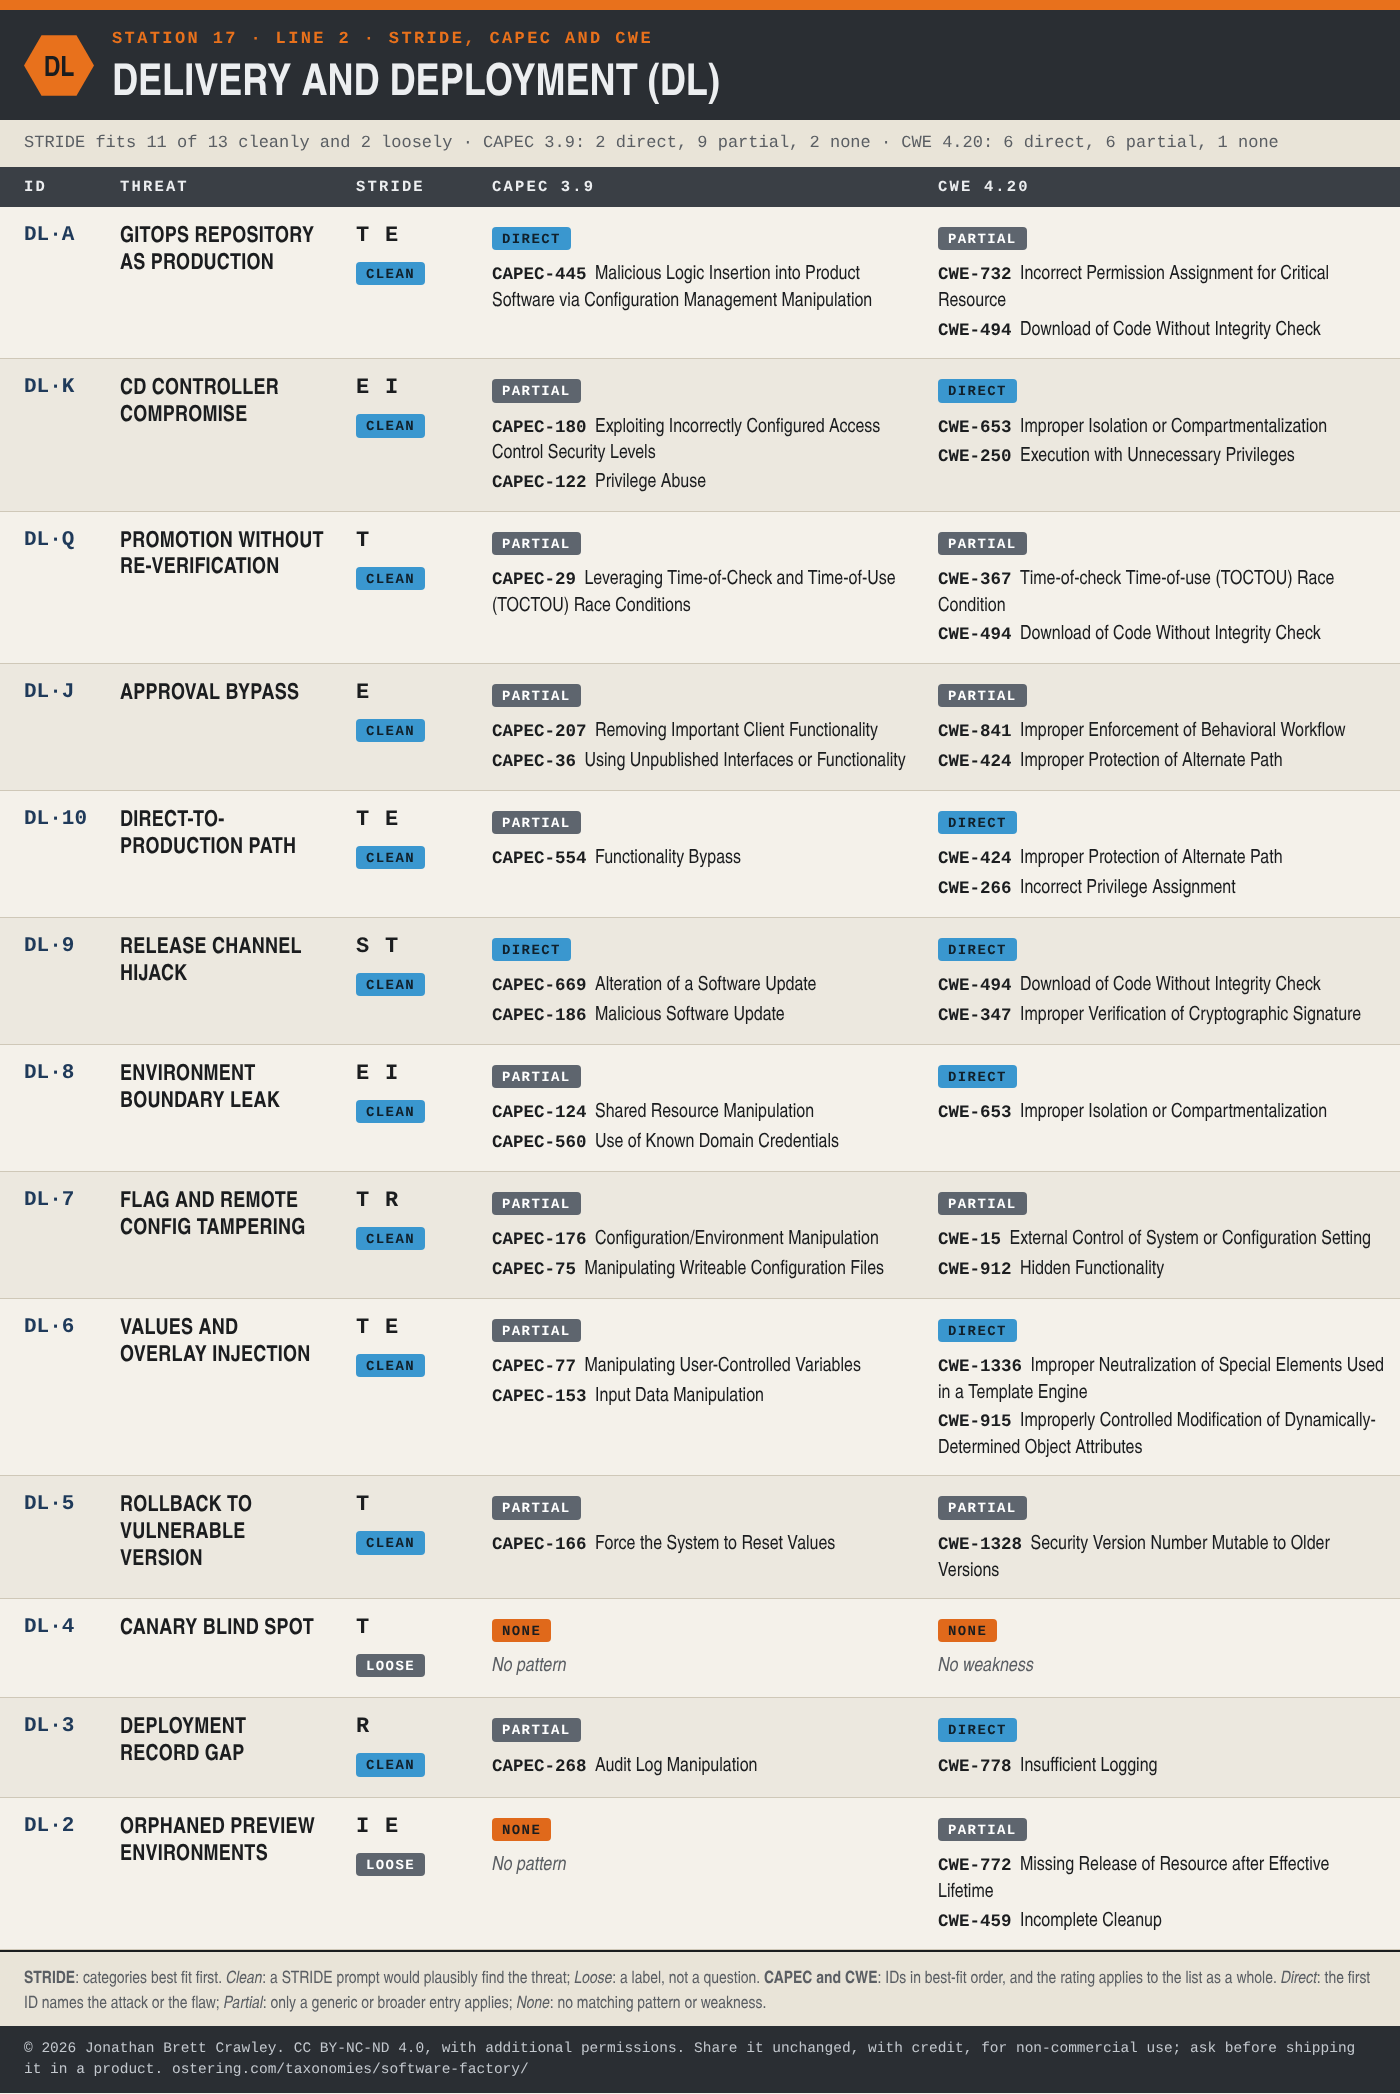
Of the 13 entries here, STRIDE fits 11 cleanly and 2 only loosely. CAPEC 3.9 has a pattern that describes 2 of them directly, only a generic parent pattern for 9, and nothing for 2. CWE 4.20 names the weakness directly for 6, has only a broader weakness for 6, and nothing for 1. The table below gives the mapping entry by entry, with the names of the CAPEC patterns and CWE weaknesses; what the mapping shows across the whole taxonomy is in Mapping the Software Factory Threat Taxonomy to STRIDE, CAPEC and CWE. The Excel, SKOS and STIX downloads carry the same mapping as text.
← Orchestration (OR) · Software factory overview · Structural hazards (T) →
© 2026 Jonathan Brett Crawley. Licensed under CC BY-NC-ND 4.0 with additional permissions: see the licence on the software factory overview.