Runners (RN)
Taxonomies › Software factory › Runners
Station 04 of 17 · Line 1, Source to Artifact · 13 threats · prefix RN
The runner is where untrusted code and the factory’s secrets share a machine. These cards cover CI controllers, hosted and self-hosted build agents, caches, artifacts passed between jobs, and the isolation between them.
Scope: Hosted and self-hosted build agents, caches, artifacts passed between jobs, isolation.
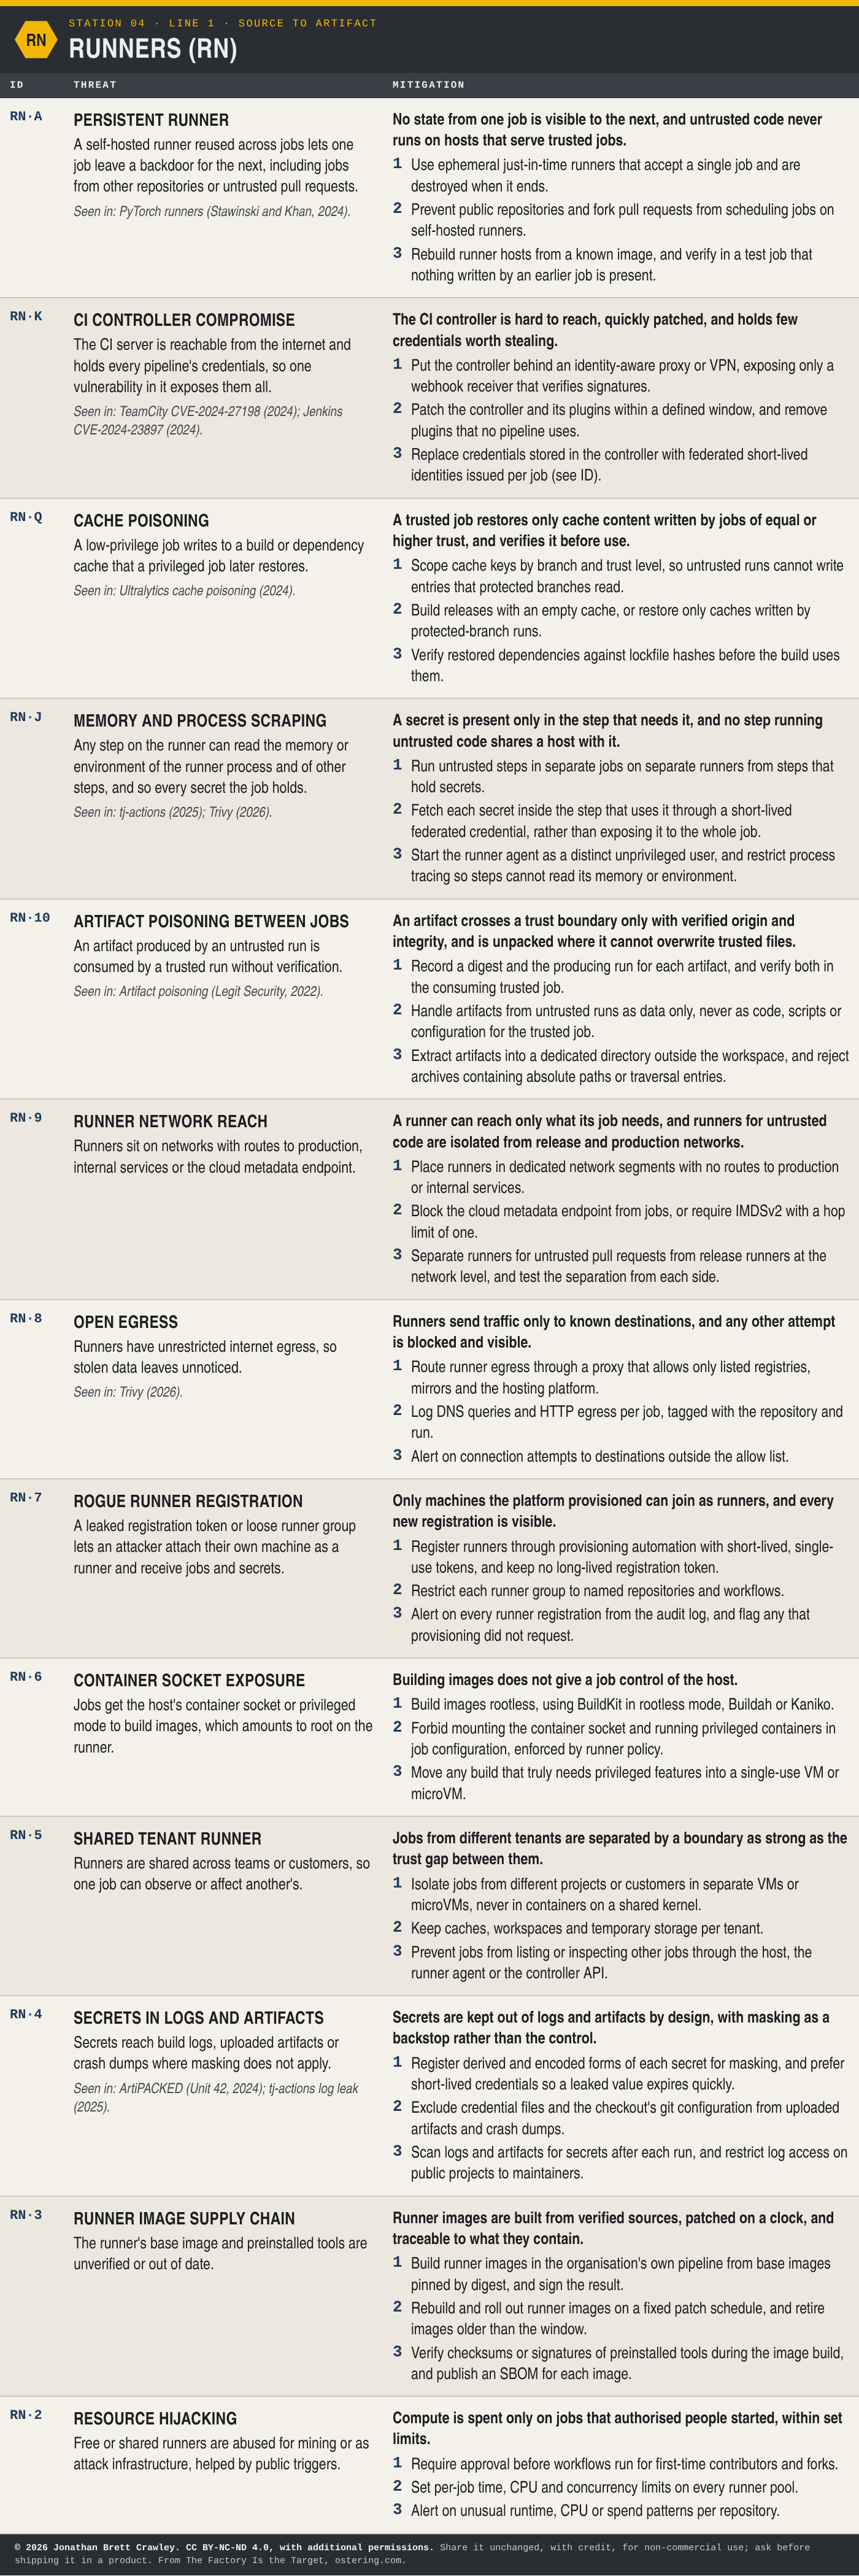
Text version: every entry on this page is in the PDF and Excel downloads on the overview page, where it can be searched and copied.
The threats
- RN·A Persistent Runner
- RN·K CI Controller Compromise
- RN·Q Cache Poisoning
- RN·J Memory and Process Scraping
- RN·10 Artifact Poisoning Between Jobs
- RN·9 Runner Network Reach
- RN·8 Open Egress
- RN·7 Rogue Runner Registration
- RN·6 Container Socket Exposure
- RN·5 Shared Tenant Runner
- RN·4 Secrets in Logs and Artifacts
- RN·3 Runner Image Supply Chain
- RN·2 Resource Hijacking
Where this station touches others
- Pipeline Definition and Runners: the definition is what the pipeline is told to do; the runner is where it executes and what survives between jobs.
Seen in the wild
- RN·A Persistent Runner: PyTorch runners (Stawinski and Khan, 2024).
- RN·K CI Controller Compromise: TeamCity CVE-2024-27198 (2024); Jenkins CVE-2024-23897 (2024).
- RN·Q Cache Poisoning: Ultralytics cache poisoning (2024).
- RN·J Memory and Process Scraping: tj-actions (2025); Trivy (2026).
- RN·10 Artifact Poisoning Between Jobs: Artifact poisoning (Legit Security, 2022).
- RN·8 Open Egress: Trivy (2026).
- RN·4 Secrets in Logs and Artifacts: ArtiPACKED (Unit 42, 2024); tj-actions log leak (2025).
Sources for each case are listed on the overview page.
STRIDE, CAPEC and CWE
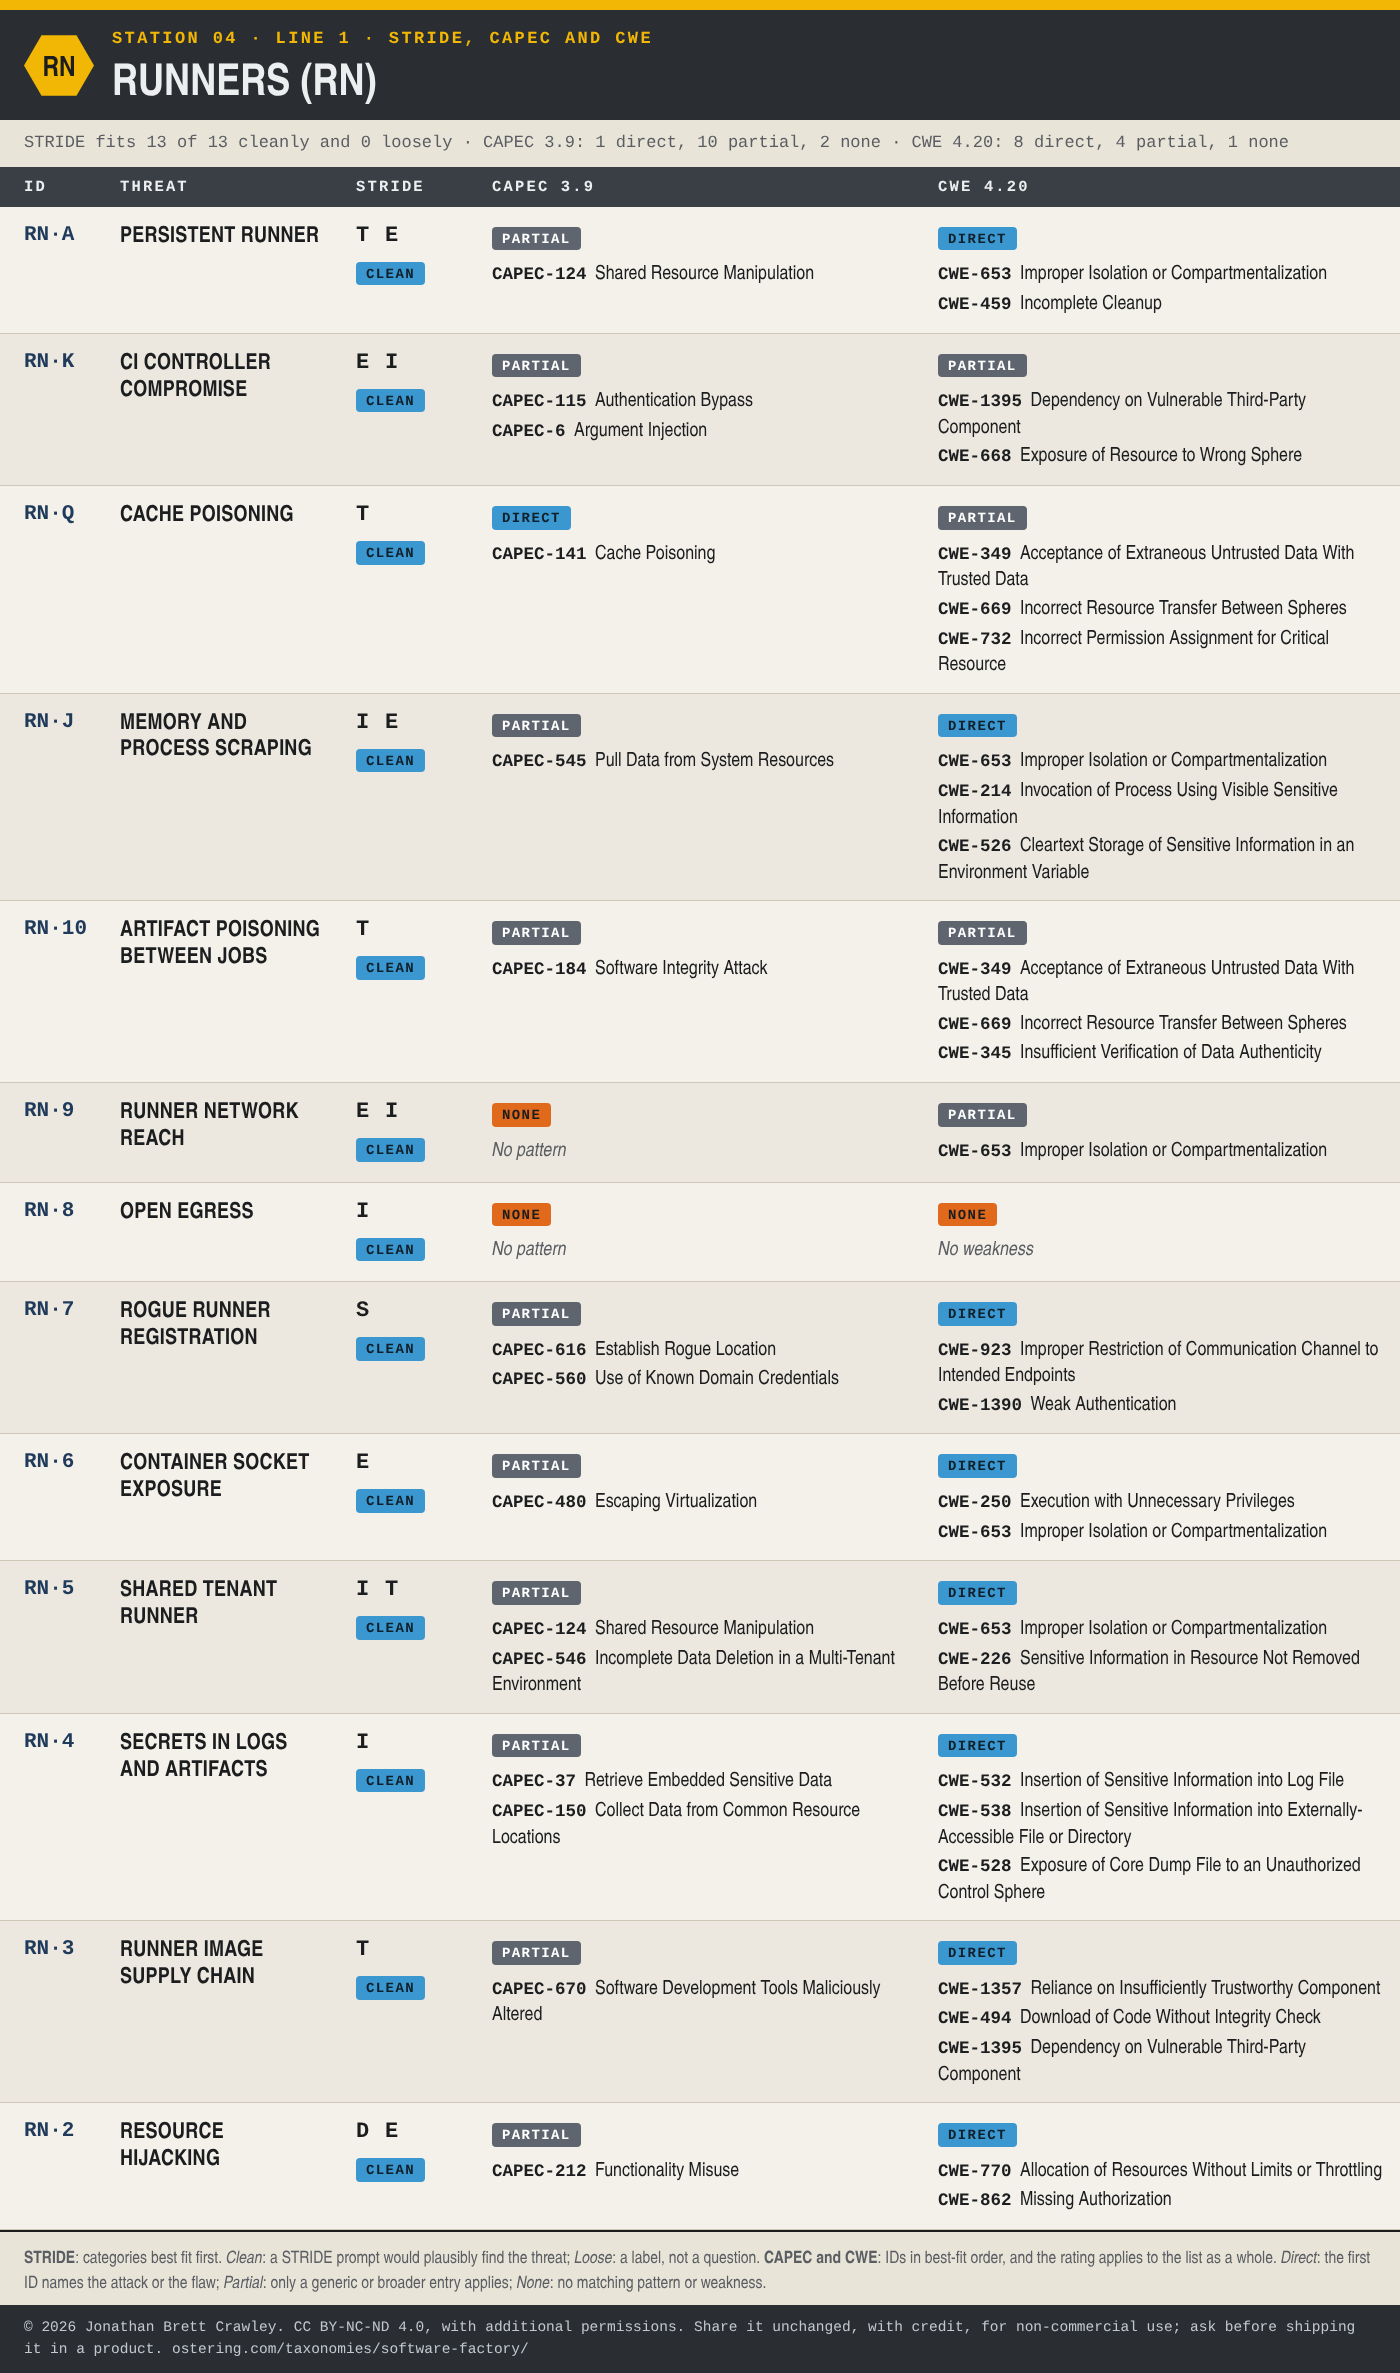
Of the 13 entries here, STRIDE fits all 13 cleanly. CAPEC 3.9 has a pattern that describes 1 of them directly, only a generic parent pattern for 10, and nothing for 2. CWE 4.20 names the weakness directly for 8, has only a broader weakness for 4, and nothing for 1. The table below gives the mapping entry by entry, with the names of the CAPEC patterns and CWE weaknesses; what the mapping shows across the whole taxonomy is in Mapping the Software Factory Threat Taxonomy to STRIDE, CAPEC and CWE. The Excel, SKOS and STIX downloads carry the same mapping as text.
← Pipeline Definition (PD) · Software factory overview · Pipeline Identity and Secrets (ID) →
© 2026 Jonathan Brett Crawley. Licensed under CC BY-NC-ND 4.0 with additional permissions: see the licence on the software factory overview.