Infrastructure as Code (IC)
Taxonomies › Software factory › Infrastructure as Code
Station 13 of 17 · Line 2, Artifact to Runtime · 13 threats · prefix IC
Infrastructure as code makes the estate reviewable, and makes whoever runs the code the owner of the estate. These cards cover Terraform and OpenTofu, Pulumi, CloudFormation and configuration management, their state, modules and providers, and the plan and apply pipeline.
Scope: Terraform and OpenTofu, Pulumi, CloudFormation, Ansible; state, modules, providers, plan and apply.
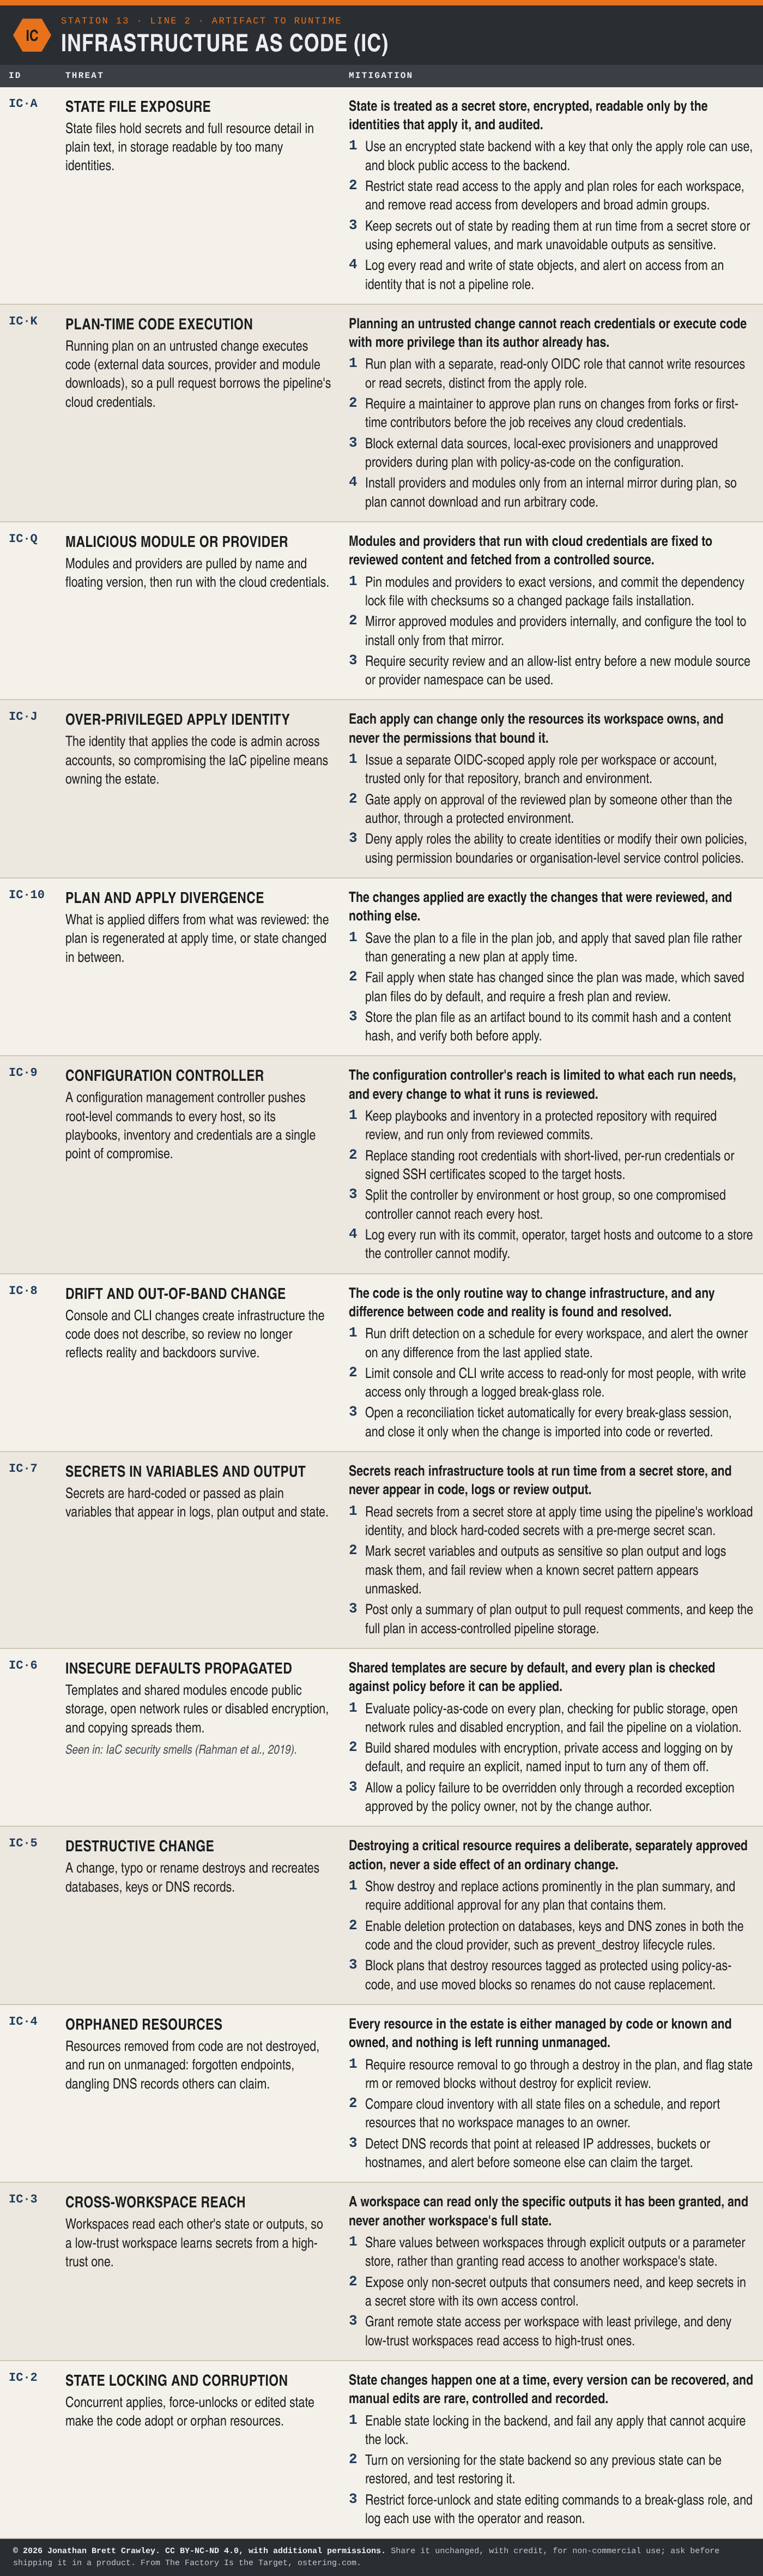
Text version: every entry on this page is in the PDF and Excel downloads on the overview page, where it can be searched and copied.
The threats
- IC·A State File Exposure
- IC·K Plan-Time Code Execution
- IC·Q Malicious Module or Provider
- IC·J Over-Privileged Apply Identity
- IC·10 Plan and Apply Divergence
- IC·9 Configuration Controller
- IC·8 Drift and Out-of-Band Change
- IC·7 Secrets in Variables and Output
- IC·6 Insecure Defaults Propagated
- IC·5 Destructive Change
- IC·4 Orphaned Resources
- IC·3 Cross-Workspace Reach
- IC·2 State Locking and Corruption
Seen in the wild
- IC·6 Insecure Defaults Propagated: IaC security smells (Rahman et al., 2019).
Sources for each case are listed on the overview page.
STRIDE, CAPEC and CWE
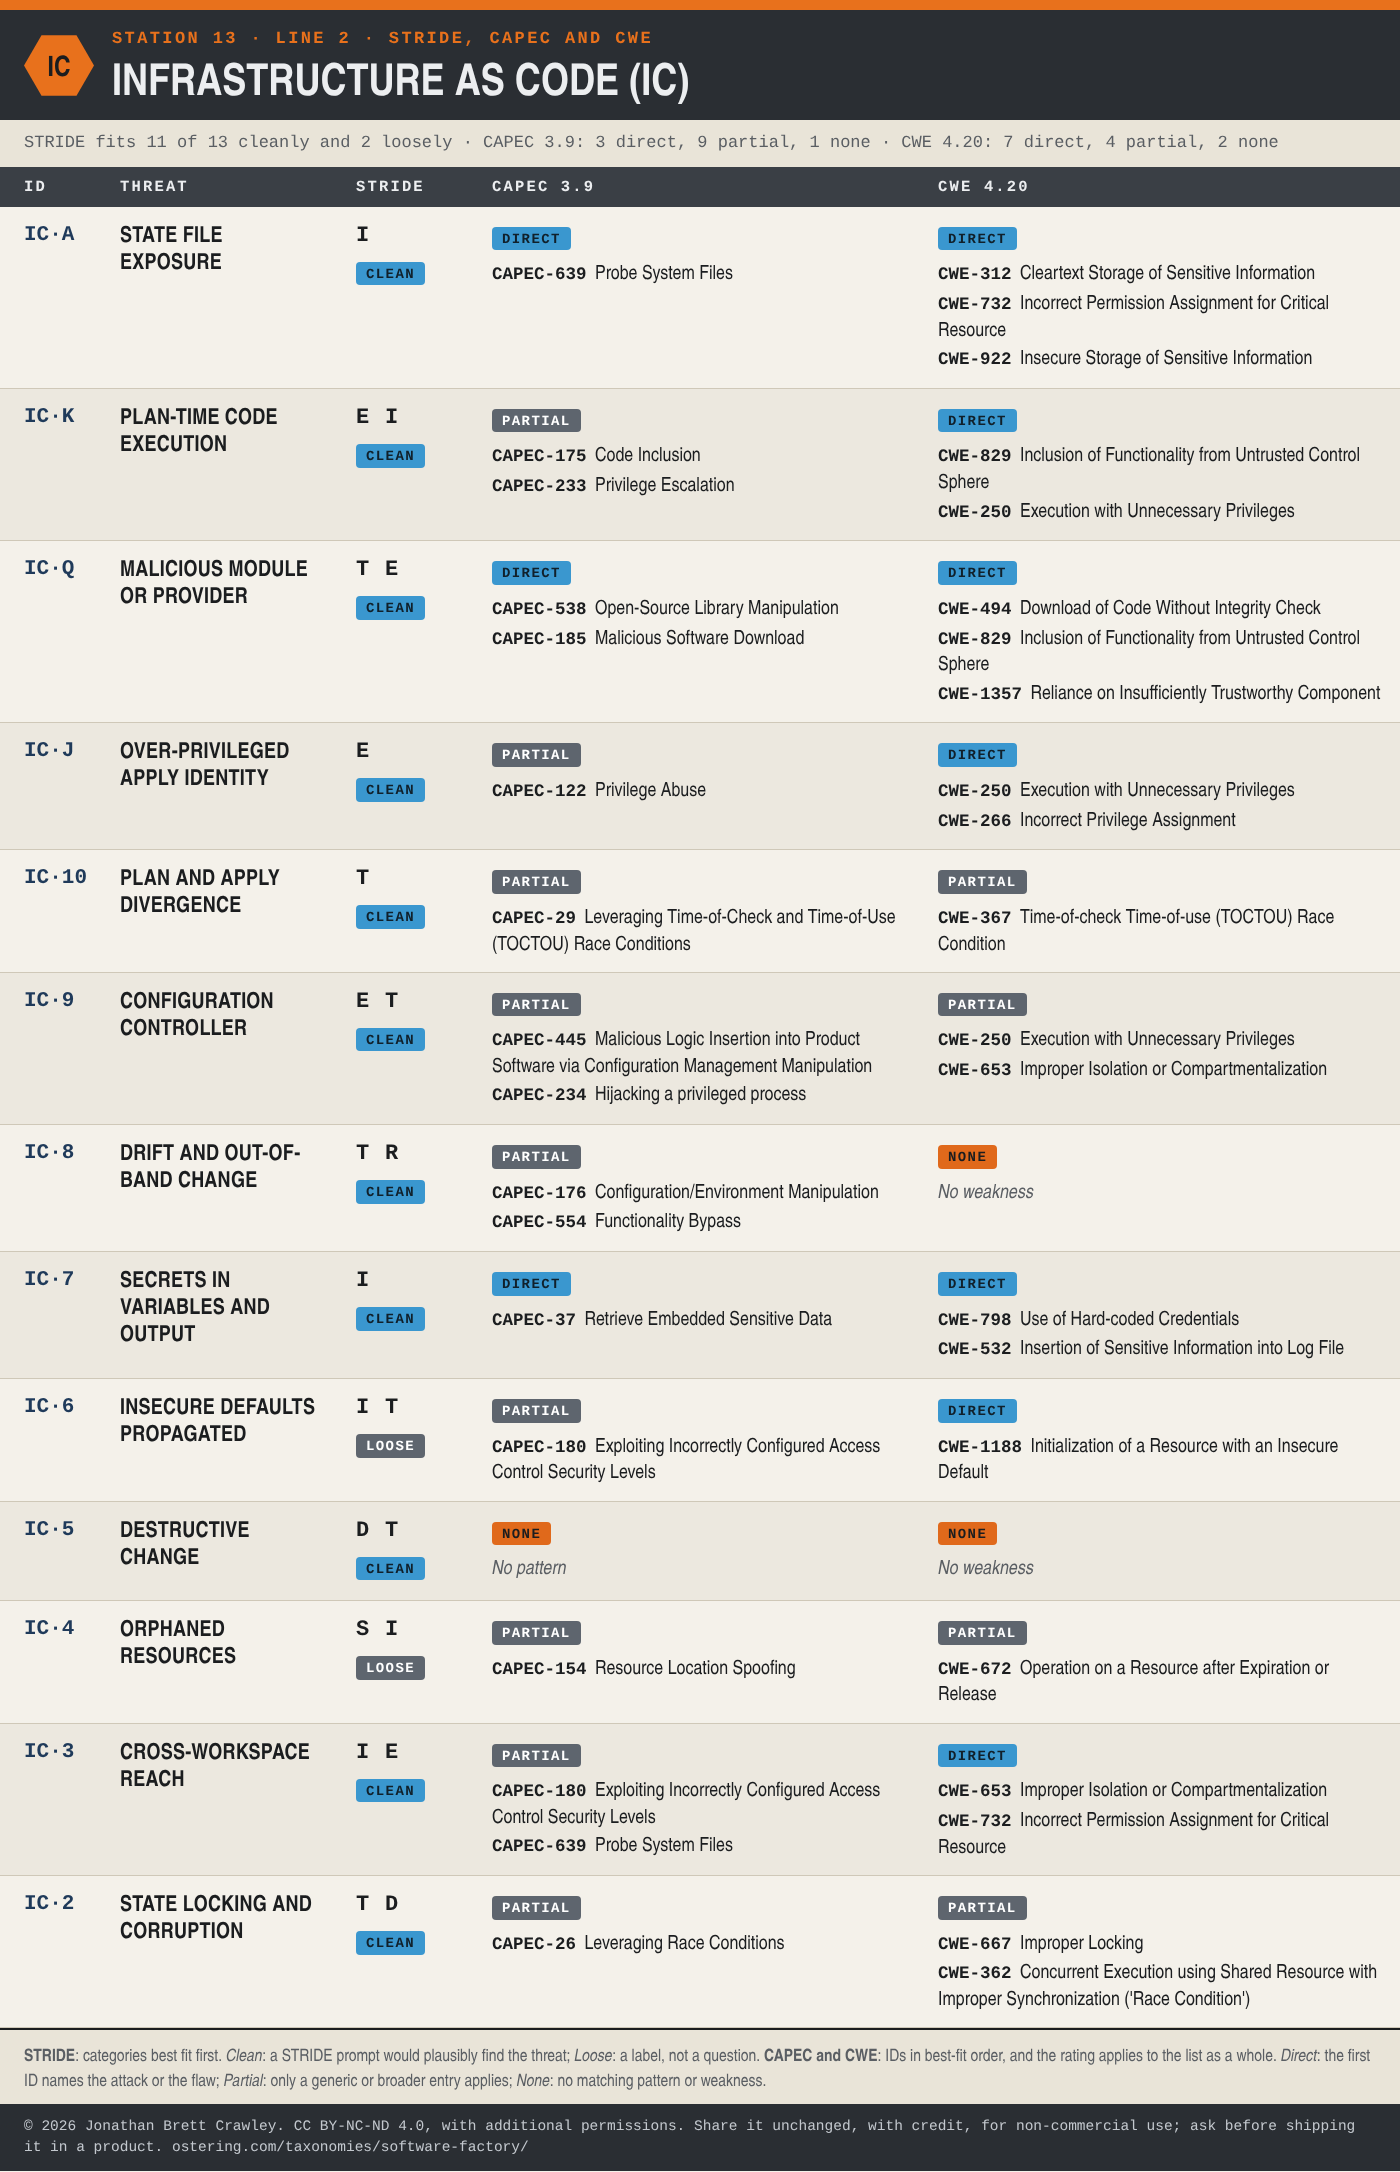
Of the 13 entries here, STRIDE fits 11 cleanly and 2 only loosely. CAPEC 3.9 has a pattern that describes 3 of them directly, only a generic parent pattern for 9, and nothing for 1. CWE 4.20 names the weakness directly for 7, has only a broader weakness for 4, and nothing for 2. The table below gives the mapping entry by entry, with the names of the CAPEC patterns and CWE weaknesses; what the mapping shows across the whole taxonomy is in Mapping the Software Factory Threat Taxonomy to STRIDE, CAPEC and CWE. The Excel, SKOS and STIX downloads carry the same mapping as text.
← SBOM and VEX (BM) · Software factory overview · Container Images (IM) →
© 2026 Jonathan Brett Crawley. Licensed under CC BY-NC-ND 4.0 with additional permissions: see the licence on the software factory overview.