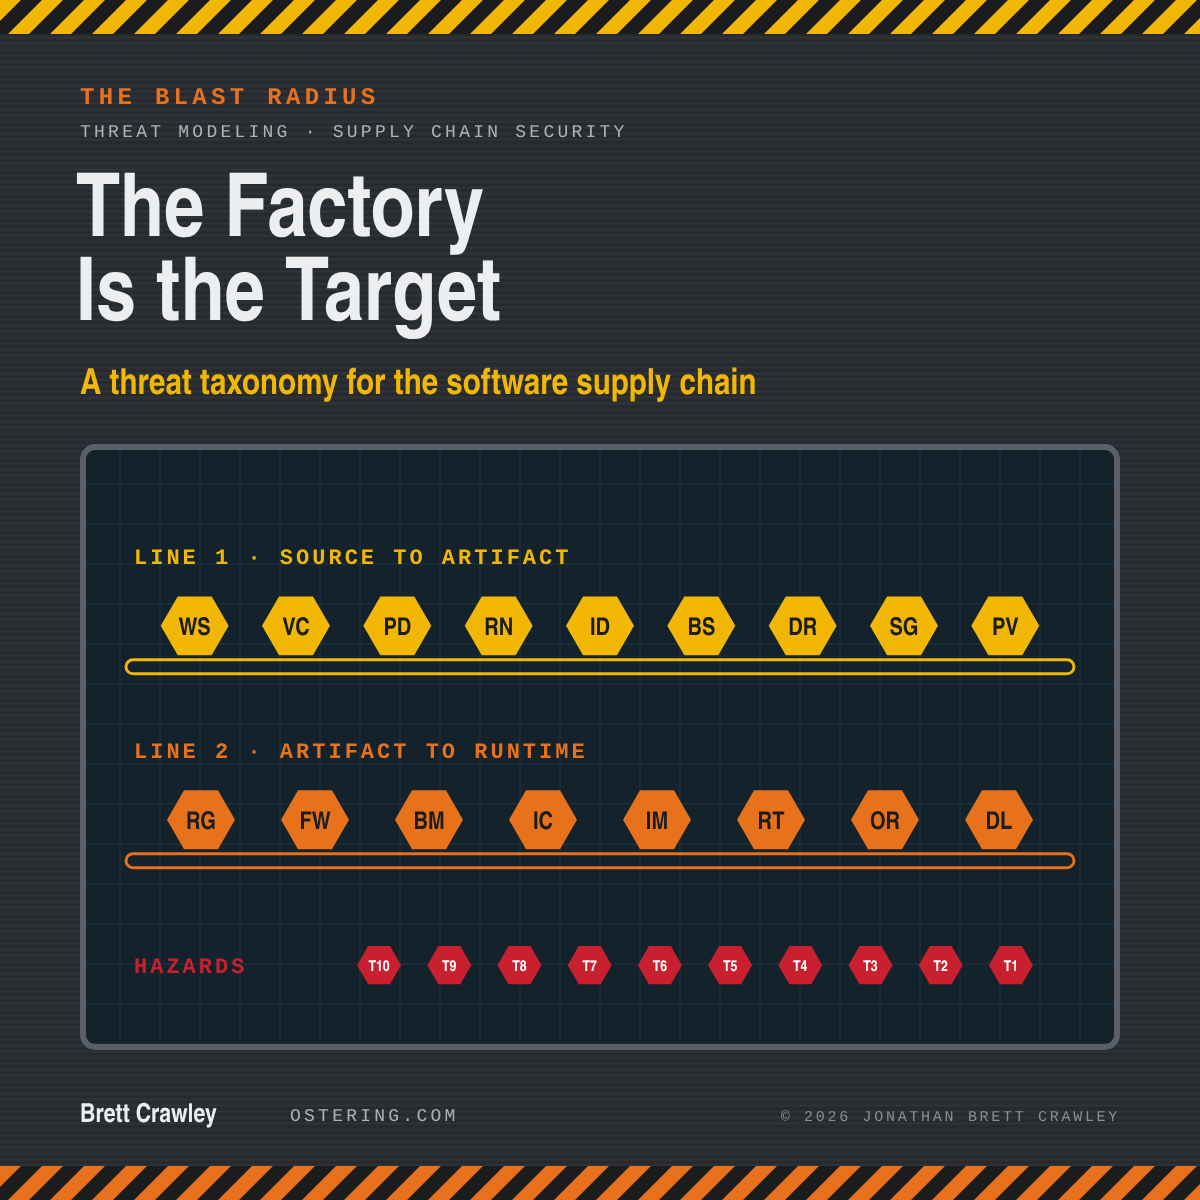
The Factory Is the Target - A Threat Taxonomy for the Software Supply Chain
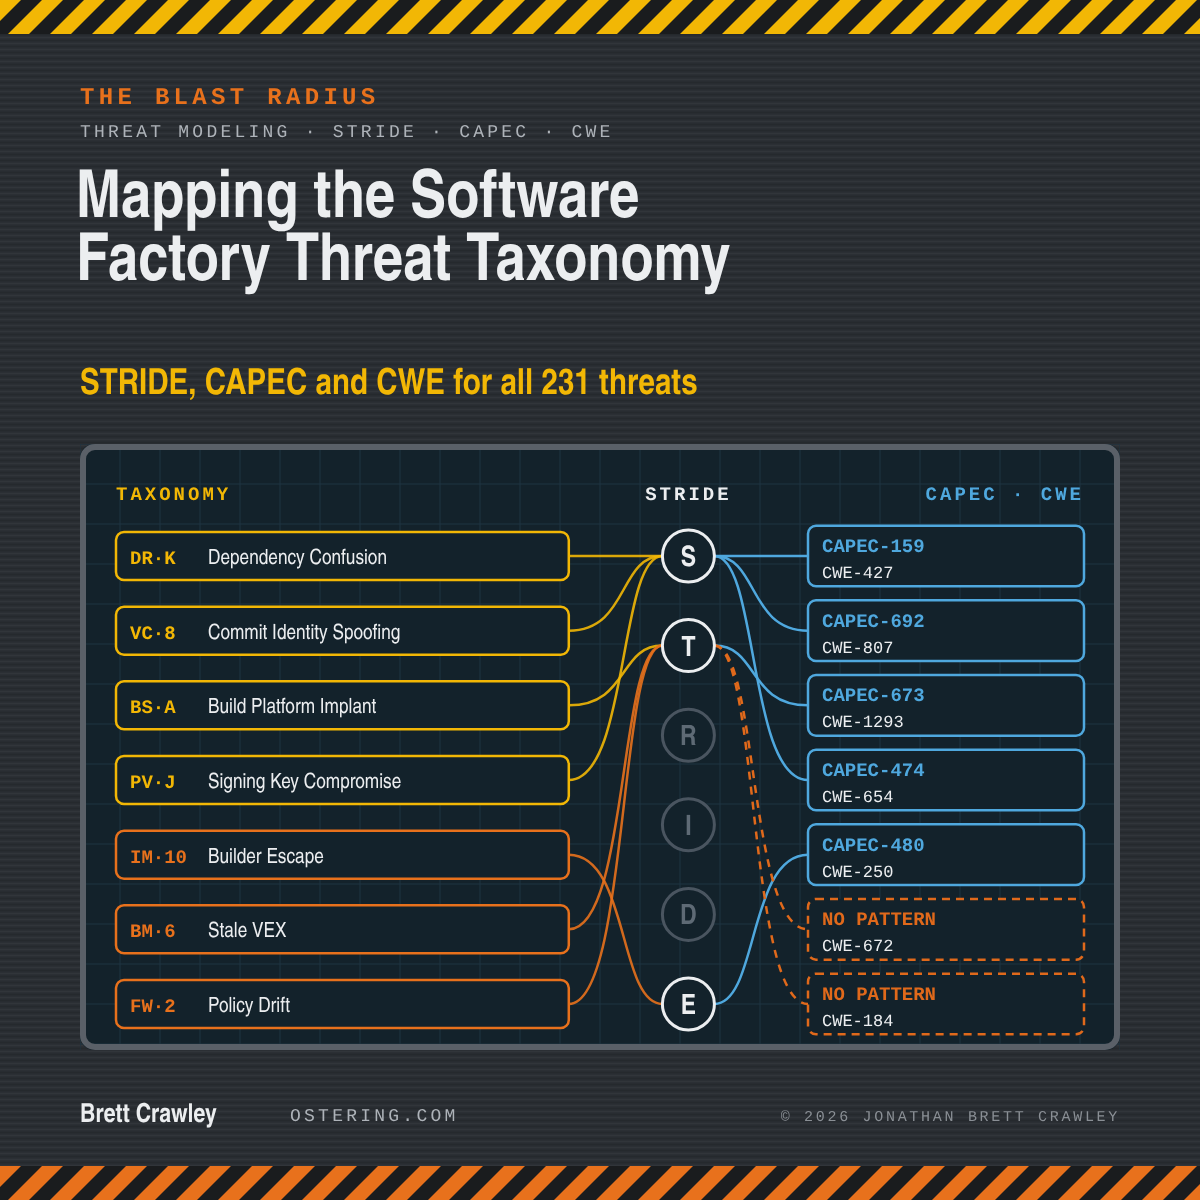
TL;DR: Most of today’s supply chain compromises start in the software factory, the machinery that turns source code into running software, and there is still no threat taxonomy that covers it end to end. I have published one: 221 threats across 17 stations of the factory, from the developer’s laptop…